Who should see sensitive information? Can untrusted input change important records? Can one employee create and approve a payment? Could a consultant’s access to one client create a conflict with another?
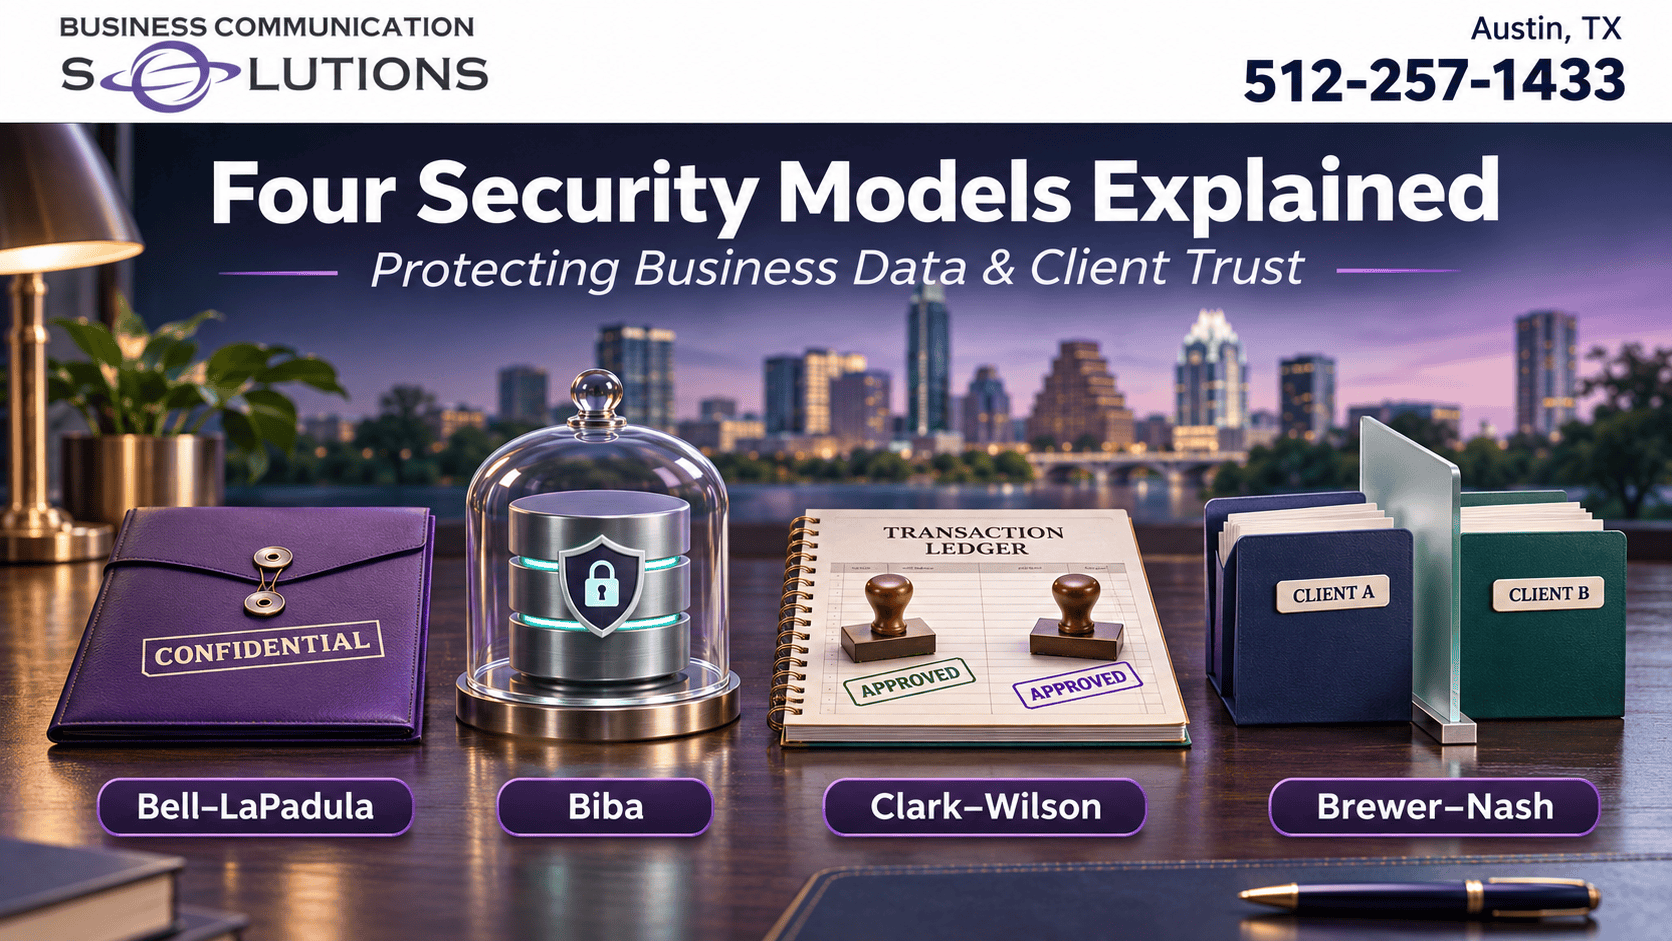
For Austin business owners, these are practical questions about permissions, software design, and accountability. Four established security models—Bell–LaPadula, Biba, Clark–Wilson, and Brewer–Nash—help explain the different rules needed to address them.
Business Communication Solutions (BCS) helps small and midsize businesses connect security decisions with their operations. Understanding these models can improve the questions you ask about your systems, even when your business does not need a formal implementation of every model.
Four security models at a glance
| Model | Primary concern | Business question | Example |
|---|---|---|---|
| Bell–LaPadula | Confidentiality | Who can read sensitive information, and where can it flow? | Label-based separation of classified information. |
| Biba | Integrity | Can less-trusted processes or data affect trusted resources? | Protecting trusted files from a lower-integrity service. |
| Clark–Wilson | Integrity through controlled transactions | Can someone change business records outside approved procedures? | Validated transfers, separate approvals, and reconciliation. |
| Brewer–Nash | Confidentiality and conflicts of interest | Does previous access make another client’s information inappropriate to access? | Restricting access to competing clients’ confidential datasets. |
A model describes security rules. A product supplies mechanisms. The product, configuration, supporting procedures, and actual enforcement determine whether those rules are implemented. The examples below identify that distinction.
Bell–LaPadula: protect information from unauthorized disclosure
Bell–LaPadula is associated with multilevel confidentiality policies. Its familiar rules are no read up and no write down. Labels can include sensitivity levels and compartments.
Illustrative military scenario: a process operating at Secret cannot read Top Secret material. A process operating at Top Secret cannot ordinarily write that information into a lower-classification destination. Authorization and need-to-know still matter.
Military and intelligence environments are classic use cases for these confidentiality concerns. It would be inaccurate to conclude that every Department of Defense system uses Bell–LaPadula.
Which Linux versions support this approach?
Red Hat documents an SELinux Multi-Level Security (MLS) policy in RHEL 9 and RHEL 10. It uses a modified Bell–LaPadula approach called write equality, restricting ordinary writes to the same sensitivity level. The relevant policy package is selinux-policy-mls.
A server running SELinux with a targeted policy is not automatically running this MLS configuration. Check the active policy and the supported workload before treating Linux as a formal multilevel system.
What about Oracle?
Oracle Label Security provides label-based row access controls for Oracle Database. It compares data labels with user authorizations using levels, compartments, and groups. This is a related confidentiality mechanism; read and write controls, exceptions, and privileged access depend on policy configuration. Ordinary Oracle database permissions alone do not establish Bell–LaPadula enforcement.
For defense contractors, CUI is unclassified information requiring safeguards. Calling a file CUI does not make it Secret or Top Secret, and a CMMC environment does not become a multilevel-security system simply by using VLANs or labels. See our information flow control guide for CMMC and SOC 2.
Biba: protect trusted resources from less-trusted influence
The strict Biba integrity model is commonly summarized as no read down and no write up. It addresses integrity rather than secrecy.
Illustrative scenario: an internet-facing service operates at low integrity while important application files have higher integrity. The service cannot overwrite those trusted files. A higher-integrity process also cannot freely read lower-integrity information under the strict model.
A direct implementation: FreeBSD mac_biba
FreeBSD offers the mac_biba mandatory access-control policy. Administrators can label subjects and objects and configure integrity restrictions. This is an explicit implementation example, but it is an optional configured policy rather than something to assume on every FreeBSD installation.
A partial example: Windows Mandatory Integrity Control
Windows Mandatory Integrity Control (MIC) uses integrity levels. Its default no-write-up policy helps stop a lower-integrity process from writing to a higher-integrity object.
MIC is not the full strict Biba model. Windows does not generally enforce Biba’s no-read-down rule. Browser process integrity also depends on the application and configuration; avoid assuming every browser process runs at Low integrity.
Clark–Wilson: protect records through approved transactions
Clark–Wilson fits commercial integrity problems: valid changes, authorized users, separation of duties, and evidence of what happened.
Illustrative bank-transfer scenario: a teller submits a transfer through an authorized application. The application validates the request, applies business rules, and updates protected records. The teller cannot simply edit the account-balance table. Separate approval applies where required, and records support reconciliation.
- Transformation Procedure (TP): an authorized procedure that changes protected data while preserving defined integrity conditions.
- Constrained Data Item (CDI): protected data subject to those integrity rules.
- Unconstrained Data Item (UDI): input not yet subject to the protected-data constraints.
- Integrity Verification Procedure (IVP): a procedure that checks whether protected data is in a valid state.
Separation of duties and audit records help prevent one person from creating and concealing an improper transaction. Certification and enforcement rules are part of the model; an approval button alone is insufficient.
Product illustration: SAP S/4HANA documents payment approval and journal-entry verification workflows. These features illustrate relevant mechanisms. They do not prove that every SAP installation implements the complete Clark–Wilson model.
Brewer–Nash: restrict access when client interests conflict
Brewer–Nash, historically known as the Chinese Wall model, addresses conflicts of interest using access history and defined conflict classes.
Illustrative consulting scenario: a consultant initially may access either Client A’s or competing Client B’s confidential dataset. After accessing Client A’s information, the consultant is blocked from the conflicting Client B dataset. Access to a nonconflicting client in a different conflict class may remain available.
The model also restricts writes to prevent indirect information transfers. It is more than a static folder permission, and it does not automatically reset when an engagement ends.
A related product: Microsoft Purview Information Barriers
Purview Information Barriers can restrict communication and collaboration between incompatible groups in Teams, SharePoint, and OneDrive. These controls address related information-barrier needs, such as separating organizational groups with conflicting interests.
However, configured segments do not automatically implement Brewer–Nash’s history-based access rules. Describe this as a related control rather than claiming that opening a document automatically changes Microsoft 365 permissions. Explore our Microsoft Purview setup and support services.
How Austin businesses can use these ideas
Start with the business problem before choosing a product:
- Sensitive information: identify who needs access and which destinations are permitted.
- Trusted records: identify unvalidated inputs and how they become approved information.
- Important transactions: define permitted procedures, independent approvals, validation, and audit evidence.
- Client conflicts: identify incompatible engagements and how access restrictions are enforced and reviewed.
Document who owns each decision, test the controls, and review exceptions. A written policy should match what users and administrators can actually do.
Discuss security architecture and risk with BCS
Business Communication Solutions helps businesses in Austin, Cedar Park, Round Rock, Georgetown, Pflugerville, and surrounding communities review access, network separation, Microsoft 365 security, and operational risks.
Start with a free initial cybersecurity risk assessment conversation. Detailed architecture reviews, technical testing, implementation, and documentation are scoped separately. For audit preparation, explore our SOC 2 readiness and gap assessment support.
Call 512-257-1433 to discuss your Austin business’s security priorities.
Technical references
- Red Hat: Using Multi-Level Security in RHEL 10; RHEL 9 SELinux guide.
- Oracle Label Security.
- FreeBSD Handbook: Mandatory Access Control.
- Microsoft: Mandatory Integrity Control.
- NIST workshop report on integrity policy and Clark–Wilson.
- SAP: Payment Items Approval Workflows.
- Brewer and Nash: The Chinese Wall Security Policy.
- Microsoft: Learn about Information Barriers.
Reviewed November 16, 2026. Product capabilities and enforcement depend on version, configuration, scope, and supporting procedures.