Practical education, trusted sources, and clear next steps for business owners, employees, and IT teams in Austin, Houston, and Lampasas.
Cybersecurity is a shared responsibility. Understanding your role is the first step toward protecting your business.
InfraGard is an FBI partnership with members of the private sector focused on protecting U.S. critical infrastructure. It brings people together through education, information sharing, networking, and workshops about emerging threats and technologies.
Its membership includes business leaders, IT professionals, security personnel, and other participants who contribute industry knowledge. Visit the official website to learn about the program and current membership application requirements.
The FBI’s Office of Private Sector supports dialogue and engagement with businesses. For questions about private sector engagement, the FBI directs businesses to the private sector coordinator at their local field office.
Business security benefits from cooperation. Organizations understand their operations and risks; law enforcement contributes investigative expertise and threat information. The video below introduces this shared responsibility.
CISA is the U.S. agency focused on cybersecurity and infrastructure security, with a mission that also includes emergency communications. Its public resources help businesses understand threats and strengthen their defenses.
For small and medium-sized businesses, CISA offers guidance on cybersecurity roles, incident response planning, and supply chain risks, along with resources your IT team can use.
Start with CISA’s Secure Our World guidance:
Watch for suspicious messages and requests, and use your organization’s reporting process.
Give each account its own strong password.
Add another layer of protection to account sign-ins.
Install security updates to address known weaknesses.
These habits give owners, employees, and IT teams practical ways to contribute to shared security. Assign responsibility for implementation and review progress regularly.
Hiring an IT provider, buying security software, or joining an information-sharing program does not remove the need for leadership and employee involvement. Each participant needs a clear role, and someone must verify that the work is getting done.

Identify critical operations and sensitive information, approve policies and resources, assign responsibility, and make decisions about business risk.

Follow security policies, complete awareness training, verify unusual requests, and report suspicious messages or activity promptly.

Carry out the agreed security work, document coverage and gaps, maintain systems, manage access, and test backups and response procedures.

Protect the parts of a service covered by their agreements. Your organization still needs to understand its responsibilities for accounts, permissions, configurations, and data.

Support threat awareness, collaboration, and investigation. Businesses remain responsible for their own day-to-day safeguards. Shared responsibility should mean clear ownership. Write down who performs each task, who reviews it, and who takes over when that person is unavailable
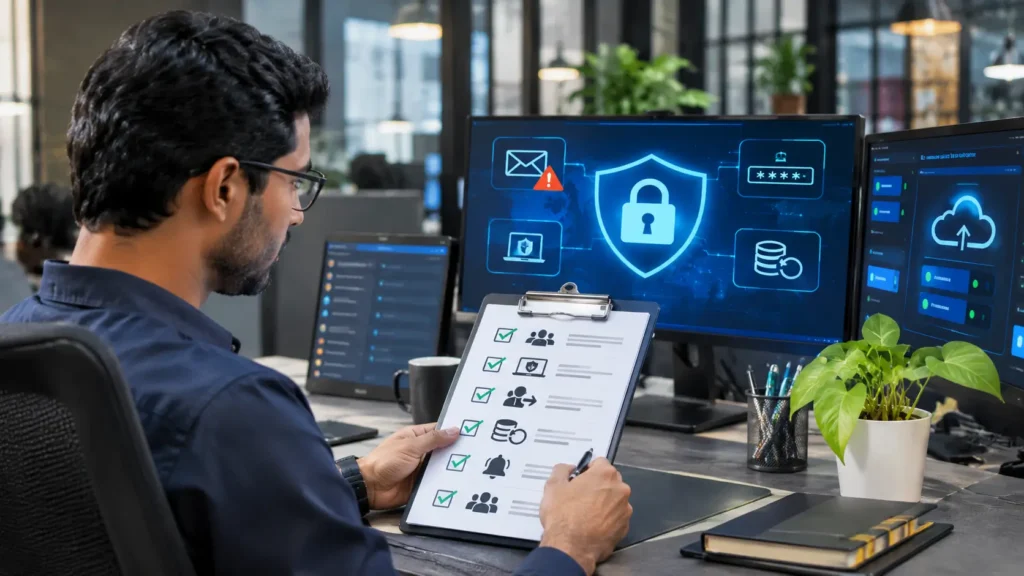
Start with a few questions that expose gaps between expectations and actual coverage:
For example, a business owner may assume that backups are being tested while the IT provider’s agreement covers only backup monitoring. A written responsibility list and a scheduled review help catch that gap before a disruption.
practical education for your team.
practice roles and decisions before an incident.
connect security decisions to business priorities.
explore device management and corporate policies.
Business Communication Solutions helps organizations review their security needs, clarify IT responsibilities, and put practical safeguards in place. Whether you need managed IT support or a second set of eyes alongside your existing IT team, start with a conversation.
Austin: 512-257-1433
Houston: 281-815-8784
Lampasas: 512-865-4000
Sources: Official InfraGard website, FBI Office of Private Sector, and CISA. Featured resources and videos are provided for education. Their inclusion does not imply government endorsement of BCS.
Find answers about support, pricing, our 30-day trial, security monitoring, Microsoft 365, backups, risk assessments, SOC 2, and CMMC readiness for Austin and Houston businesses.