SOAR stands for Security Orchestration, Automation and Response. In simple terms, it connects your security tools and helps automate the routine steps that happen after an alert. Instead of your team manually moving from one system to another, SOAR can follow predefined workflows and trigger the right response actions.
With SOAR Cybersecurity Austin, you can:
Turn security alerts into coordinated action without even making your team handle every step manually. Less manual chasing, more consistent security response.
An alert comes in. Someone now needs to check it, connect the dots, decide what is important, and take action. When you multiply that by your security tools, users, devices, after-hours alerts, and manual response, it’s easy to see how it becomes an obstacle.
A security alert comes in? Now someone has to figure out what it means and what to do next. With SOAR, much of that routine work can happen through automated workflows, helping your team respond to threats without chasing every step manually.
An Alert Comes In:
Your SIEM, EDR, email security, or another connected tool flags suspicious activity and sends the alert into the SOAR workflow.
SOAR Connects the Dots:
SOAR pulls in relevant security data and threat intelligence, giving your team more context before deciding what action is needed.
The Right Action Starts:
Predefined playbooks can trigger approved actions such as isolating an endpoint, blocking a malicious IP, or escalating an incident for review.
Your Team Takes Over When Needed:
Automation handles the repeatable steps while your security team focuses on investigation, judgment, and incidents that need a closer look.
Automatically start response workflows when suspicious emails are flagged, helping your team investigate and contain email threats without handling every step manually.
When EDR detects suspicious activity, SOAR can trigger an approved workflow to isolate the affected device and send the incident for review.
Unusual login activity can trigger predefined workflows that gather account details, flag potential compromise, and escalate the incident when human review is needed.
SOAR can connect with firewalls and other security controls to trigger approved actions against malicious IP addresses, domains, or other known threats.
Instead of manually researching every alert, SOAR can gather threat intelligence and related security data to give your team better context.
When an incident needs human attention, SOAR can notify the right person, create a ticket, and move the case through your defined response process.
Turn security alerts into automated workflows by connecting SIEM detection with predefined response workflows.
Connect phishing alerts with workflows that support email investigation, threat removal, and incident escalation.
Connect cloud security events with workflows for account activity, suspicious access, and response coordination.
Enrich security alerts with threat intelligence, helping your team understand suspicious indicators before taking action.
Connect endpoint detection with response workflows to help investigate suspicious devices and trigger approved isolation actions.
Help trigger approved blocking actions when connected security tools identify suspicious IP addresses or network activity.
Bring identity alerts into response workflows to help investigate unusual logins and potential account compromise.
Automatically create tickets, send notifications, and route incidents to the right person for further investigation.
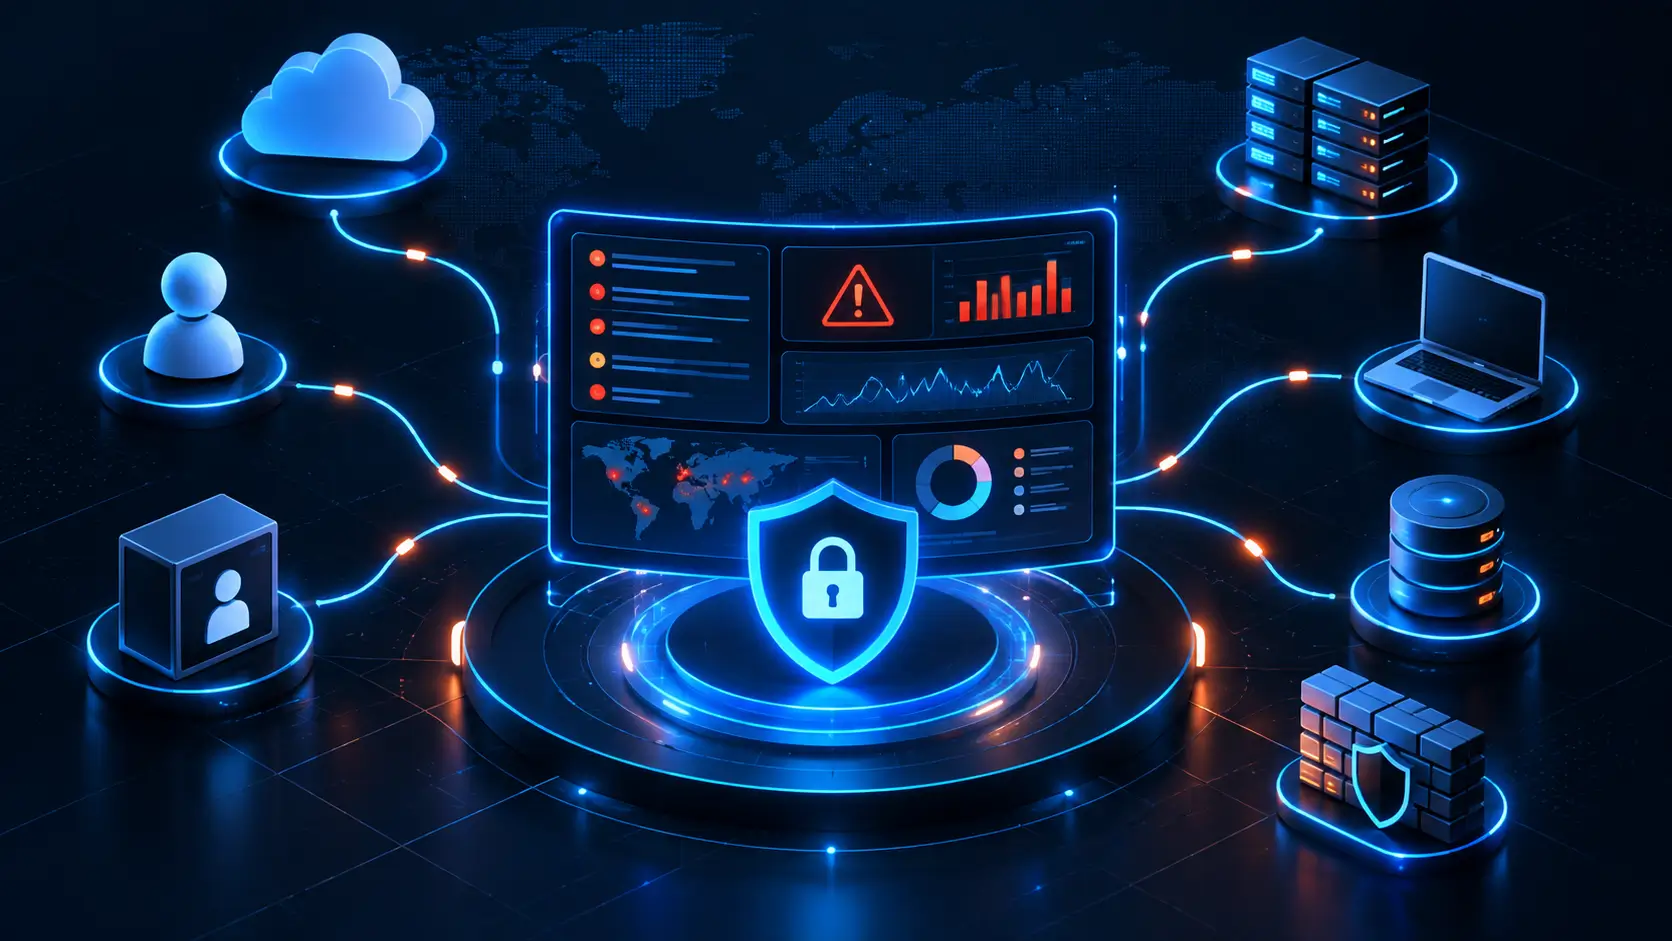
Your SIEM helps detect and connect suspicious activity. SOAR helps decide what happens next by automating predefined response steps, reducing manual work and helping your team act faster.
For example, if your SIEM detects repeated failed logins from an unusual location, SOAR can trigger a predefined workflow for account review, notification, or another configured response action
SOAR can help contain threats quickly through approved workflows, such as isolating compromised devices, blocking malicious IPs, restricting accounts, or even removing harmful emails.
With carefully defined rules and human approvals where needed, BCS helps you contain threats while reducing disruption to your business.
These security tools work together, but each has a different job… SIEM helps find the signal. SOAR helps automate the response. MDR/SOC brings security professionals into the monitoring and investigation process. Get SIEM Services and MDR/SOC Monitoring to build a more connected security approach.
| SIEM | SOAR | MDR / SOC | |
|---|---|---|---|
| Main role | Detect & correlate | Automate response | Monitor & investigate |
| Focus | Security visibility | Response workflows | Human security expertise |
| Remember it as | See | Act | Watch & investigate |
Cybersecurity isn’t always something you can fix from a dashboard. Sometimes a compromised laptop, firewall, server, network, or Wi-Fi setup needs someone on-site.
BCS has supported Central Texas businesses for 20+ years, with a Cedar Park/Austin team providing both remote and on-site support when security issues become physical.
SOAR connects your security tools and automates predefined response steps after an alert.
It reduces repetitive security work and helps small teams respond to alerts more consistently.
Yes. SOAR can connect with SIEM, EDR, email security, firewalls, and other tools to coordinate response workflows.