

Your subcontractor needs to review a sensitive document. Your employee needs to work remotely. But you do not want business files downloaded to a personal laptop, copied to a USB drive, or printed at home.
Can you let someone work with information while keeping ordinary file storage and processing inside a controlled environment? Yes—with a carefully designed combination of access controls, remote applications, document permissions, and monitoring.
Three terms often come up: secure data enclave, restricted virtual desktop, and virtual data room. They describe related approaches, but they are not interchangeable.
What is a secure data enclave?
In this context, an enclave is a defined computing environment for sensitive work, separated from other systems through appropriate technical and administrative controls. It may contain selected applications, storage, identities, and security services.
The design should answer practical questions: who can enter, which devices and applications they can use, where information is stored, how it can leave, and who reviews activity.
An enclave is an architecture and operating model, rather than a single product. A separate folder or VLAN alone does not establish a complete secure environment.
VDI vs. a virtual data room
| Approach | Typical use | What to evaluate |
|---|---|---|
| Secure data enclave | Keep a defined sensitive workflow within a controlled boundary. | Applications, identities, storage, network paths, administration, monitoring, and data handling. |
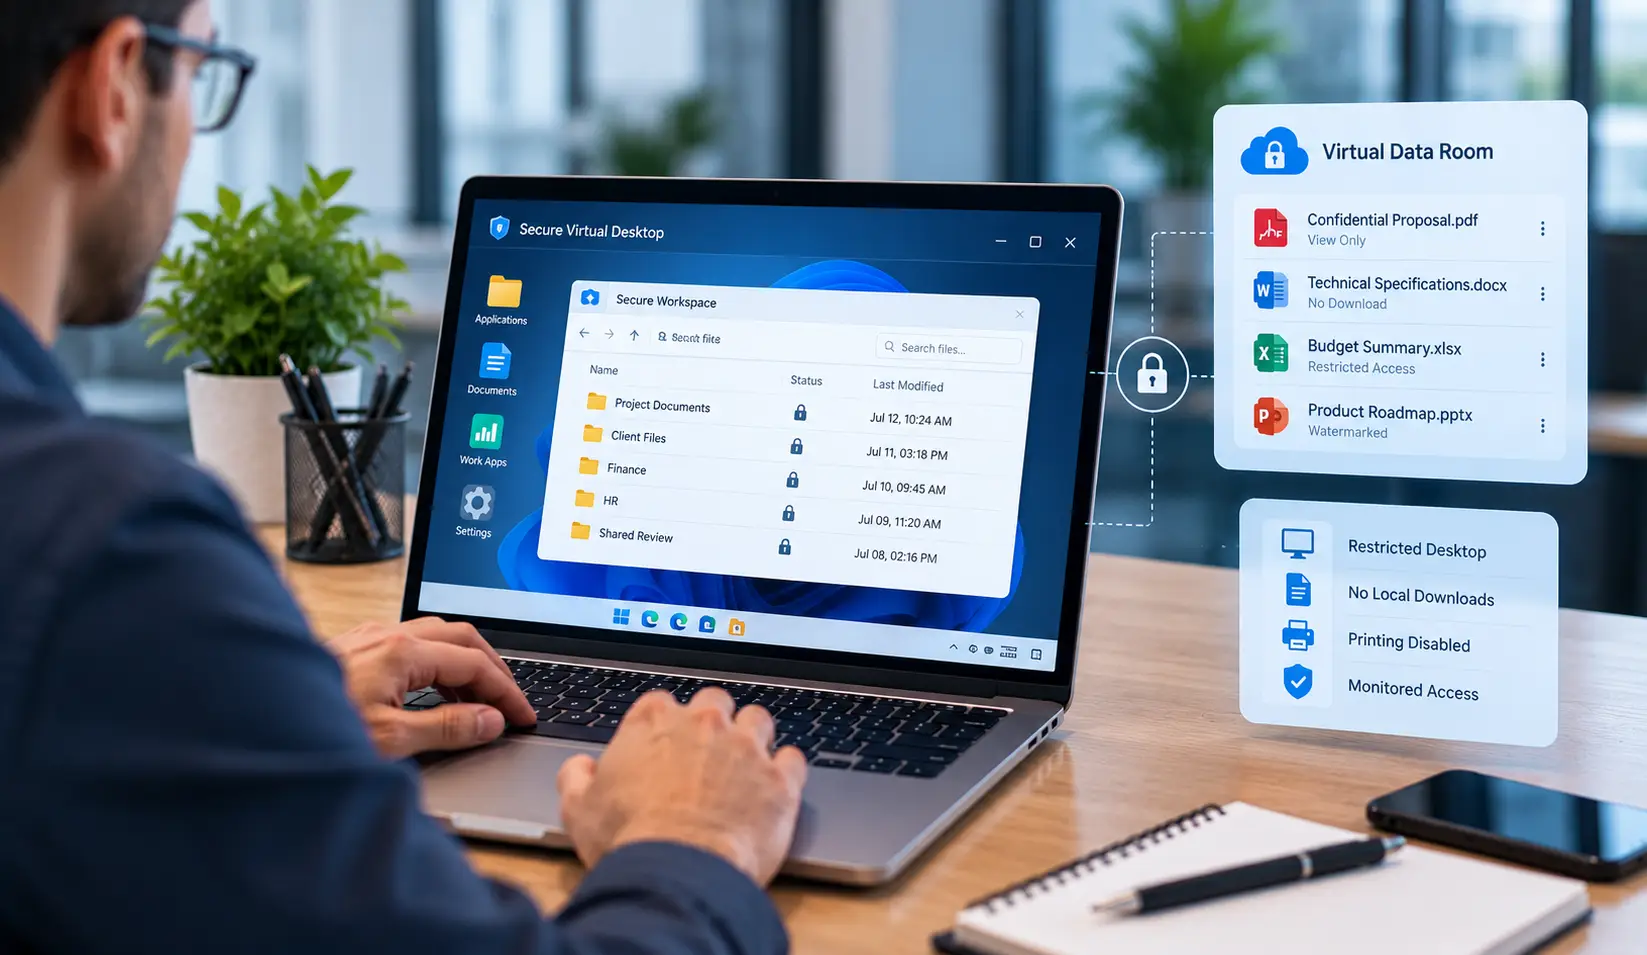
| Restricted virtual desktop or remote application | Let users work in applications running on centrally managed systems. | Clipboard, local drives, printing, peripheral redirection, session access, and outbound sharing. |
| Virtual Data Room (VDR) | Share selected documents with outside reviewers or collaborators. | Supported file types, viewing and download permissions, watermarking, expiration, and audit records. |
Some VDRs support editing and collaboration as well as review. “Data room” does not automatically mean view-only. Likewise, a virtual desktop does not automatically block local downloads.
Tools and vendors to evaluate
These are examples to compare against your workflow, rather than claims that a product alone provides compliance.
Microsoft Azure Virtual Desktop and Windows 365
These options provide remote Windows desktops or applications. Microsoft documents controls for clipboard transfer, drive redirection, and printer redirection.
They are worth evaluating when users must perform work in business applications rather than simply view documents. Review application compatibility, identity requirements, licensing, operating costs, and the supported client devices.
Citrix Virtual Apps and Desktops
Citrix is another option for delivering controlled applications and desktops. Its policy framework includes redirection controls, while App Protection provides additional protections on supported clients. Confirm the exact version, licensing, and endpoint support for the proposed controls.
Ideals Virtual Data Room
Ideals documents granular permissions for supported document types, including browser viewing, watermarks, download permissions, and Fence View. Fence View obscures much of the document while allowing the portion near the cursor to be read.
This is an option to evaluate for controlled document review. Test the actual files your subcontractors use; permission behavior can vary by file type.
Kiteworks Virtual Data Rooms
Kiteworks describes need-to-know permissions, watermarked viewers, expiration policies, activity records, and DLP integration. Ask the vendor to demonstrate the specific view-only and export restrictions you require, including how they work across web and mobile access.
Can we really say “no data reaches the remote device”?
That wording is too absolute. A remote device must receive and display information for a person to work with it. The useful goal is to restrict local file copies, processing, and export paths according to a defined design.
A better description is: “Users work inside a controlled remote environment, with local download, clipboard, drive, and printing functions restricted as required.”
Screen-capture protection also has limits. Microsoft explains that its protection depends on supported operating-system features and APIs, is not DRM-level protection, and should be combined with other controls. Watermarking can discourage misuse and help trace a session, but it does not physically stop someone from photographing a screen. See Microsoft’s screen-capture guidance.
VDI Blocks Downloads—But What About a Phone Camera?
A restricted VDI session can block digital export paths. It cannot physically stop someone pointing a separate camera at the screen. For Austin and Houston contractors handling CUI, these are different risks that need different controls.
The CMMC VDI endpoint exclusion is conditional: the client must be configured so no CUI processing, storage, or transmission occurs beyond keyboard/video/mouse interaction. Verify the implementation rather than assuming that purchasing VDI makes every connecting device out of scope.
| What happens? | Where does the CUI copy go? | What needs review? |
|---|---|---|
| Screenshot saved on the local VDI client | The client now holds a local CUI copy. | Local storage and capture capabilities undermine reliance on the keyboard/video/mouse-only exclusion. Reassess the endpoint and affected controls. |
| A separate smartphone photographs CUI displayed in VDI | The photograph creates a CUI copy on the phone. | Review the phone, photo library, automatic synchronization, backups, messages, and any other destinations. |
| The original VDI client after a separate-camera photograph | Photography alone does not demonstrate a local digital export to that client. | Verify its actual configuration and data flows. Do not promise that it automatically remains out of scope or automatically becomes a CUI Asset solely because another device took a photo. |
Does a photo automatically invalidate the VDI boundary?
Do not reduce the answer to an automatic pass or fail. The separate phone holding CUI and the original VDI endpoint require distinct analysis. Our distinction between optical capture and local digital export is an architectural interpretation of the data flow—not an official ruling guaranteeing a particular assessment result.
Unauthorized photography may reveal a handling, physical-security, personnel, or incident-response issue even when digital redirection controls work. Review authorization, actual exposure, implemented safeguards, and applicable requirements. A policy violation and a technical scope question can both require attention.
What controls should the business consider?
- Restrict digital exports: enforce and test clipboard, local drive, file-transfer, printer, USB, and screenshot restrictions on each approved client and platform.
- Define permitted work locations: consider who can see the screen, nearby cameras, shared workspaces, and unattended sessions.
- Set camera and recording rules: prohibit unauthorized photographs and recordings, explain approved alternatives, and train employees and subcontractors.
- Use supported capture protection and watermarking: these can reduce supported software capture or help trace a session; they do not guarantee prevention of external-camera photography.
- Prepare for a captured copy: identify who receives reports, investigates destinations, contains exposure, and coordinates evidence preservation and any required notifications.
If a photo is discovered, follow the incident-handling process. Determine whether it synchronized or was shared, and coordinate containment and evidence preservation. Do not assume deleting the visible photo removes every copy.
Evidence should show what actually works
Keep configuration records, platform-specific test results, approved-location rules, training records, and the response procedure. A statement that screenshots are disabled does not prove every supported client enforces the restriction. A watermark is a deterrence and traceability measure, not an access-control boundary.
Microsoft explicitly discusses physical-camera capture and recommends watermarking to discourage it. Its screen-capture protection relies on supported operating-system features and APIs and is not DRM-level protection.
Primary references: 32 CFR 170.19: CMMC scoping and Microsoft screen-capture protection guidance.
BCS helps Austin and Houston businesses review remote-access workflows, scope assumptions, capture restrictions, and responsibilities. Explore CMMC readiness support or call Austin: 512-257-1433 | Houston: 281-815-8784.
Blocking downloads is only one part of the design
Review every permitted way information can leave the environment:
- Clipboard: text, images, and files in either direction.
- Local storage: mapped drives, downloads, synchronization, and supported browser or client transfer features.
- Printing: physical printers and virtual printers such as Print to PDF.
- Peripherals: USB and other redirected devices where supported.
- Sharing from inside the session: personal email, cloud storage, chat, websites, and applications that allow uploads.
- Other access paths: direct links, alternate clients, mobile applications, and administrative accounts.
Disabling local drive mapping does not address every other path. Citrix specifically documents the risk of export through redirected software printers.
Approve the routes the business needs, restrict the others, and test the result. DLP can support this work where the relevant applications, locations, and policies are covered.
What does this mean for BYOD?
A restricted desktop or document viewer can reduce the need to distribute business files to personal devices. It does not automatically establish that every personal device is suitable.
Define permitted endpoints, authentication, client software, session behavior, and response procedures. Consider endpoint compromise, shared computers, local capture, and who can access an unattended session. A thin client or company-managed endpoint may be a better fit for some workflows.
Users also need a practical process for authorized exports. If a subcontractor must deliver a completed drawing, decide how that output is reviewed and transferred without opening unrestricted sharing everywhere.
Read our related article on asset management, BYOD, and network access control.
Can restricted VDI help with CMMC scope?
Potentially. The official CMMC FAQ describes a condition under which an endpoint hosting a VDI client can be out of scope: it must not process, store, or transmit CUI beyond the keyboard/video/mouse interaction sent to the client.
This is a conditional scoping provision, not an automatic benefit of buying VDI. Document actual data flows and verify the configuration. A virtual data room should not be assumed to qualify under a VDI-specific provision.
The hosted environment and its supporting services still need evaluation against applicable requirements. Review cloud-service obligations, administrative access, logging, and other information-handling paths. Where a C3PAO assessment is required, discuss the proposed scope and supporting evidence with the assessment organization.
Keeping a subcontractor’s endpoint outside a particular boundary also does not automatically remove the subcontractor’s separate contractual obligations.
Explore our CMMC gap assessment and implementation support and CMMC asset categories guide.
Audit the access and monitor the environment
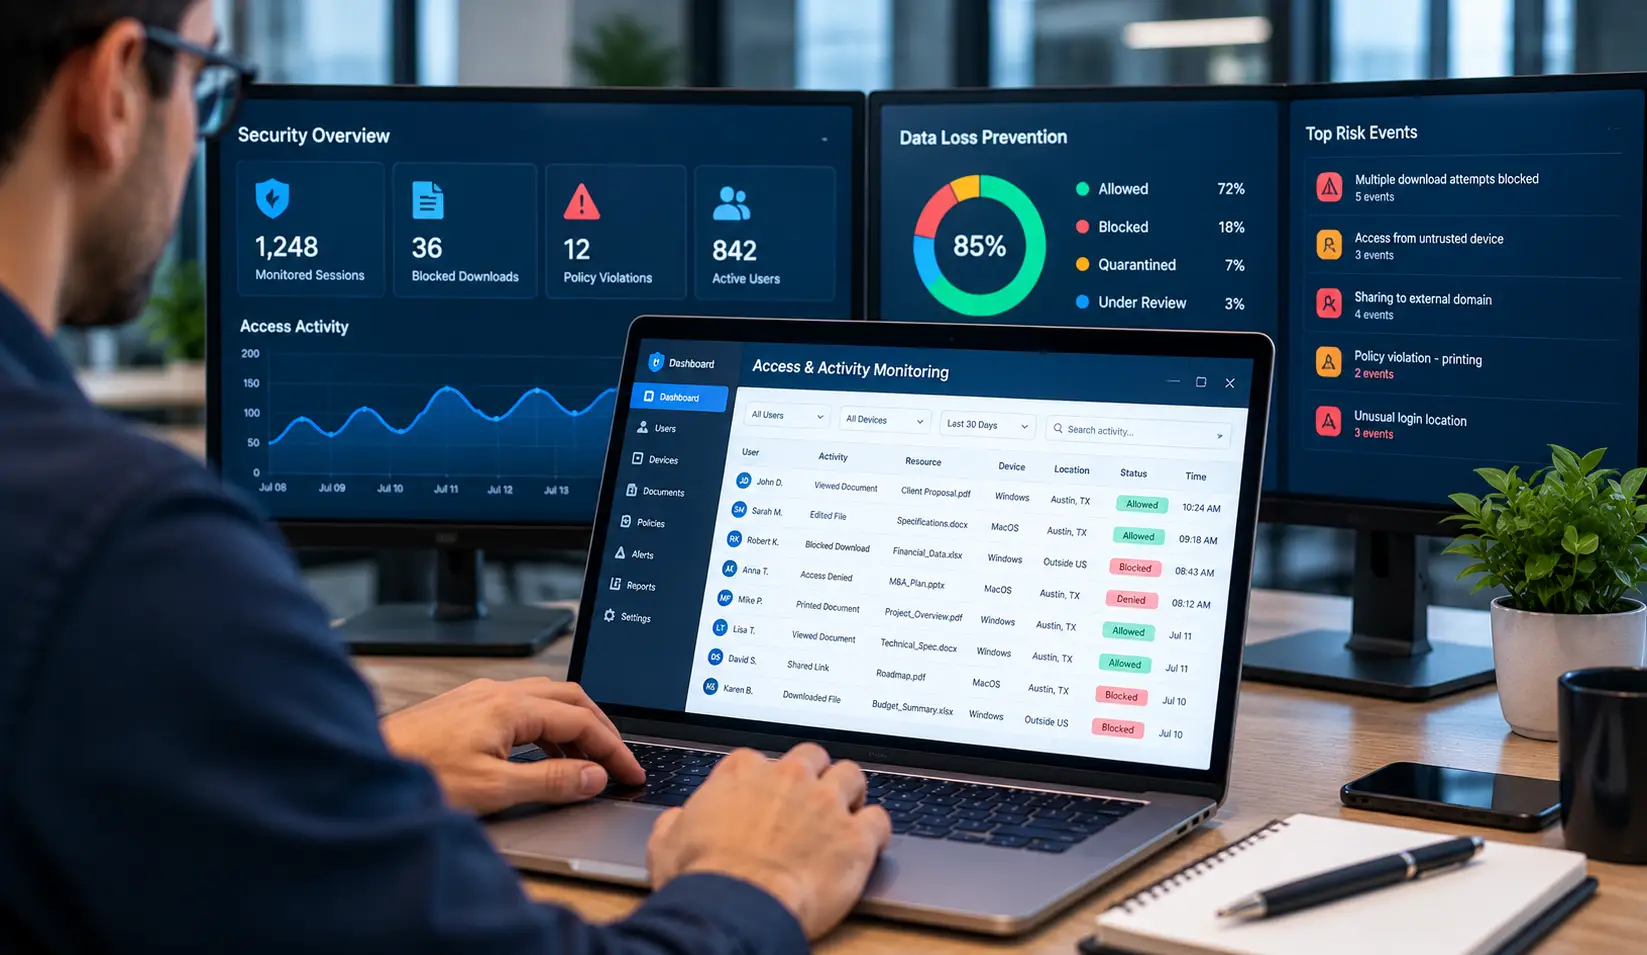
Plan which records you need: authentication, permission changes, document access, export attempts, session activity, and administrative actions. Available events depend on the selected products and integrations.
Assign an owner to review alerts, preserve evidence, and respond. Confirm log retention and access permissions. Session recording, if used, creates another potentially sensitive data store that needs its own handling rules.
Microsoft Purview can contribute audit and data-protection capabilities for supported workloads. It does not automatically record every event in an unrelated VDR or desktop platform. See our monitoring tools guide for the distinction between recording, detection, and response.
How should a small business choose?
- Define the task: document review, editing, analysis, or application access.
- Identify the information: business confidentiality, customer requirements, and applicable contract obligations.
- Map the users and devices: employees, subcontractors, administrators, managed endpoints, and BYOD.
- Set allowed actions: viewing, editing, printing, downloading, uploading, and approved output delivery.
- Pilot representative work: test real file types, clients, performance, accessibility, and export restrictions.
- Document and maintain: record responsibilities, exceptions, evidence, and changes after updates.
For document review, begin by evaluating a VDR. For work requiring full applications, evaluate restricted desktops or published applications. Choose the architecture around the work and risk, then verify the controls.
Frequently Asked Questions
1. What is the difference between a secure data enclave and a virtual data room?
A secure data enclave is a controlled computing environment designed to protect sensitive workflows, applications, and information. A virtual data room is primarily used to share selected documents with authorized reviewers. The right option depends on whether users need document access or a broader working environment.
2. Can VDI prevent users from downloading sensitive files?
VDI can restrict local drive access, clipboard transfers, printing, and other export paths when the relevant controls are configured. However, VDI alone does not guarantee that all copying or information leakage is prevented.
3. Is a virtual data room completely download-proof?
No. Download restrictions and viewing protections depend on the platform, document type, client, and configuration. Screen photography and other capture methods may still be possible, so businesses should combine permissions with appropriate monitoring and handling policies.
4. Can a subcontractor access sensitive documents from a personal laptop?
Potentially, if the business approves the device and configures suitable authentication, session controls, and access restrictions. A restricted desktop or document viewer can reduce local file storage, but it does not automatically make every personal device secure.
5. Can using VDI reduce CMMC assessment scope?
In certain circumstances, a VDI client endpoint may qualify for exclusion from scope under applicable CMMC scoping guidance. This depends on the actual data flows and configuration. Using VDI does not automatically remove an endpoint or the hosted environment from scope.
6. What security controls should businesses evaluate for a restricted virtual desktop?
Review clipboard and drive redirection, printing, USB access, authentication, session controls, outbound sharing, logging, and administrative access. Test the configuration with representative applications and file types before relying on it.
7. Should a business choose VDI or a virtual data room?
A virtual data room may suit controlled document review and external collaboration. VDI or published applications may be more suitable when users need to work in full business applications. Choose based on the task, sensitivity of the information, required controls, and operating costs.
Secure remote-work planning in Austin and Houston
Business Communication Solutions helps businesses review sensitive workflows, identity and device requirements, network boundaries, and readiness gaps. We can work with your internal IT team and providers to plan implementation and clarify responsibilities.
Contact BCS to discuss whether a restricted remote desktop, a document-review portal, or a broader enclave design fits your project. We do not treat a vendor name or product subscription as proof of compliance.
Austin: 512-257-1433 Houston: 281-815-8784
Discuss your secure access requirements with BCS.
What do you think?
Does your business need people to receive a copy of sensitive information—or simply work with it inside a controlled environment? Which would be the bigger challenge for your team: restricting exports, supporting BYOD, or making the workflow practical?