A laptop, a firewall, a production machine, and a guest Wi-Fi device do not necessarily receive the same treatment during a CMMC assessment. For CMMC Level 2, five asset categories help define what belongs in scope and how it is evaluated.
For a small business, the goal is to keep scope simple, small, and complete. Understand what each asset does before deciding which label fits.
Only need Level 1? Start with FCI
The five-category model below applies to Level 2. Level 1 focuses on systems that process, store, or transmit Federal Contract Information (FCI), with specific exclusions such as qualifying Specialized Assets. Do not add Level 2 classification and documentation requirements to a Level 1-only business. Read CMMC Scoping Explained for Small Businesses and confirm which level your contract requires.
The five CMMC Level 2 asset categories
| Category | What it means | Level 2 assessment treatment |
|---|---|---|
| CUI Assets | Process, store, or transmit Controlled Unclassified Information | In scope; assessed against all Level 2 requirements |
| Security Protection Assets | Provide security functions for the assessment scope | In scope; assessed against requirements relevant to their capabilities |
| Contractor Risk Managed Assets | Can handle CUI, but policies, procedures, and practices establish that they are not intended to | In scope; SSP review, with limited checks when documentation or findings raise questions |
| Specialized Assets | Qualifying assets capable of handling CUI that cannot be fully secured | In scope; SSP review of risk-based management rather than assessment against other requirements |
| Out-of-Scope Assets | Cannot handle CUI, provide no security protection for CUI Assets, and are physically or logically separated | Outside assessment; be ready to justify the exclusion |
The first four categories remain in scope. Source: 32 CFR 170.19, Table 3.
CRMA vs. Out-of-Scope Assets: a practical CMMC Level 2 comparison
“We do not intend to use this computer for CUI” and “this computer is separated so it cannot handle our CUI” are different claims. Start with the asset’s actual role, information flows, and access paths—not its VLAN name.
| Question | CRMA | Out-of-Scope Asset |
|---|---|---|
| CUI capability | Can handle CUI, but established policies, procedures, and practices prohibit the intended use. | Cannot handle the organization’s CUI under the applicable exclusion criteria. |
| Separation | Physical or logical separation from CUI Assets is not required. | Physical or logical separation supports the general exclusion; the rule also recognizes a conditional restricted-VDI endpoint exception. |
| Assessment scope | Remains in scope. | Outside scope if it provides no CUI security protection and meets no in-scope category. |
| Required treatment | Asset inventory, SSP treatment, and scope network diagram. | Prepare to justify the exclusion. |
| Assessment approach | SSP review; questions raised by documentation or other findings can trigger limited checks for deficiencies. | No assessment requirements for qualifying excluded assets. |
Source: 32 CFR 170.19(c), Table 3. The examples and validation steps below are practical applications, not a prescribed universal configuration checklist.
Example: office workstation versus internet-only guest device
An office workstation used for ordinary business work may be a CRMA when its capabilities and established workflows support that classification. An instruction saying “no CUI” does not prove technical separation. If someone actually opens a CUI attachment on it, investigate the CUI handling and correct the classification and safeguards.
A visitor’s tablet on internet-only guest Wi-Fi may qualify as out of scope when the implemented boundary supports exclusion. Test the proposed design rather than assuming that a separate SSID or VLAN settles the question.
Does a different VLAN and failed ping in both directions suffice?
No. A failed ping shows only that an ICMP test did not receive a reply. It does not establish whether HTTPS, SMB, RDP, DNS, IPv6, or another path permits communication. For a design claiming no direct communication between guest and CUI segments, examine the rules and validate separation in both directions.
- Review every route: inspect firewall rules, Layer 3 switch routing, IPv4 and IPv6, VPNs, alternate gateways, and any permitted exceptions. Blocking private IPv4 ranges alone can miss other paths.
- Test relevant services: perform authorized connection tests against representative addresses and ports; compare results with rule configuration and available logs. A timeout alone does not explain which control blocked traffic.
- Check cloud CUI access: try the actual email, SharePoint, file-sharing, and remote-access workflows using representative accounts and device conditions. An internet-only device can still reach cloud CUI if access controls permit it.
- Check indirect transfers: review forwarding, synchronization, printing, removable media, and connected devices. A network rule does not control every way information moves.
What if guest Wi-Fi shares switches, APs, or a firewall?
Classify guest endpoints separately from the infrastructure supporting the boundary. Sharing a chassis does not automatically place every connected endpoint in the same category. A firewall, switch, AP, or controller relied upon to protect the CUI environment needs its security role evaluated; do not label it out of scope simply because its management interface uses another VLAN.
Likewise, do not automatically label every shared switch only as an SPA. Examine whether it carries CUI as well as enforcing separation. DoD’s official FAQ also explains a conditional case in which otherwise separated enterprise transport components carrying properly encrypted enclave traffic need not extend the enclave’s scope. Encryption alone does not establish separation. See the official CMMC resources and FAQs.
For implementation, restrict trunk VLANs, prevent unauthorized trunk negotiation where applicable, isolate administrative access, and maintain supported configurations. An AP carrying multiple SSIDs commonly needs a restricted trunk; a guest-only wall jack commonly uses an access port. These are design choices to verify against the actual equipment.
Do shared DNS or DHCP services automatically invalidate exclusion?
Do not assume either automatic approval or automatic failure. Document where the services run, their permitted traffic, administration, and dependencies. Review whether the connection reaches an in-scope service and whether that service provides security protection. Guest DNS/DHCP on the boundary device or dedicated infrastructure can simplify the design, but public DNS alone does not establish separation.
For an internet-only guest design, block unauthorized access to switch, AP, controller, and firewall administration. Guest client isolation can reduce peer-to-peer exposure, but it does not replace the boundary between guests and CUI systems.
What evidence should support the decision?
- Classification rationale: asset purpose, owner, actual use, and why the selected category fits.
- Boundary diagram: VLANs, subnets, enforcement points, management paths, shared services, cloud applications, and approved connections.
- Configuration and validation: relevant rule exports, routing information, access-policy coverage, dated authorized test results, and resolved exceptions.
- CRMA workflows: approved handling locations, employee instructions, safeguards, and a process for investigating unintended CUI handling.
- Ongoing review: reassess after routing, identity, cloud-access, SSID, or infrastructure changes that could affect the exclusion.
Keeping an exclusion rationale and test results is useful evidence practice, not a requirement to assess every guest device as a CUI Asset. The boundary justification must match what the environment actually permits.
BCS helps Austin and Houston businesses map these paths, review classifications, and implement agreed safeguards through our CMMC gap assessment and implementation services.
CUI Assets vs. Security Protection Assets: classifying common infrastructure
A device’s product name does not determine its CMMC category. Trace what it does, which information reaches it, and which security functions the assessed environment relies upon. The examples below are practical classification considerations for CMMC Level 2.
CUI Assets handle protected information; Security Protection Assets (SPAs) provide security capabilities. Do not use “does not routinely handle CUI” as the SPA definition or ignore CUI handling merely because equipment also performs security work. Under 32 CFR 170.19(c), Table 3, CUI Assets receive assessment against all Level 2 requirements, while SPAs receive assessment against requirements relevant to their capabilities. Implementation and evidence may span multiple system components.
| Asset or service | Role to evaluate | Important qualification |
|---|---|---|
| AD DS domain controller / Microsoft Entra ID | Identity, authentication, and access enforcement can support SPA treatment. | Entra ID is not an AD DS domain controller. Examine actual services and data; hosting CUI files introduces CUI handling. Keeping production file shares off domain controllers is a hardening recommendation. |
| Firewall / VPN gateway | Boundary enforcement, filtering, remote-access protection, and inspection. | Trace tunnel termination, decryption, inspection, packet capture, and logging. Do not assume every firewall is only an SPA because traffic is encrypted elsewhere. |
| Managed or unmanaged switch | CUI transmission and, where implemented, VLAN separation, ACLs, or network admission. | A managed switch is not automatically only an SPA. An unmanaged switch is not automatically exempt. Record actual traffic and security dependencies. |
| Backup server / storage repository | Systems receiving or storing CUI backups have a CUI-handling role. | Encryption protects a backup; it does not erase its CUI status. Separate the storage, processing, orchestration, and administration functions. |
| Backup management console | Security-related configuration, credentials, and access may support SPA treatment. | Verify whether recovery previews, restores, cached files, exports, or support workflows expose CUI. “Console only” is not sufficient evidence. |
| Endpoint protection / EDR / MDR | Malware defense, detection, investigation, and containment. | Review sample uploads, collected files, memory captures, and investigation artifacts for CUI—not just ordinary telemetry. |
| Patch / vulnerability management | Configuration enforcement, remediation, and vulnerability visibility. | Review privileged access, stored credentials, remote execution, collected output, and provider responsibilities. |
| PKI / RADIUS / network authentication | Certificates, authentication, and network admission protecting the assessed environment. | Identify administrators, keys, configuration data, and dependent services. |
| SIEM / centralized logs | Security monitoring and audit information supporting protection. | Logs can include document contents, sensitive query output, or other CUI. Inspect what is actually ingested and retained. |
| Printer / scanner / multifunction device | Printing or scanning CUI introduces CUI handling; evaluate Specialized Asset eligibility where appropriate. | A device meeting exclusion criteria may be out of scope. Technical isolation does not automatically make it a CRMA. |
| Administrative jump host | Controlled administration can provide a security protection function. | Check session displays, clipboard, file transfers, recordings, and caches for CUI. A “management only” label does not settle its treatment. |
| MDM / Intune services | Security configuration, device policy, recovery-key management, and access signals. | Assess the services actually used, their permissions, collected data, and administrative access; a tenant name alone does not define the boundary. |
Encrypted transit is not a blanket exemption
DoD’s CMMC FAQ recognizes a conditional case where enterprise networking components carrying properly encrypted traffic from an otherwise logically separated enclave need not extend that enclave’s assessment scope. Encryption alone does not create logical separation. Distinguish transport outside the enclave from equipment relied upon to enforce the enclave’s security boundary. Consult the official CMMC resources and FAQs when documenting the architecture.
Do all CUI backups require FIPS encryption at rest?
Do not turn a protection requirement into a universal product requirement. NIST SP 800-171 Revision 2, 3.8.9 requires protection of backup CUI confidentiality at storage locations; its discussion permits cryptography or alternative physical controls. Requirement 3.13.16 addresses CUI confidentiality at rest. When cryptography protects CUI confidentiality, 3.13.11 requires FIPS-validated cryptography. The full design and other applicable requirements still matter.
For example, evaluate a backup kept within a controlled onsite storage area differently from data sent to cloud storage or media transported offsite. Verify the transmission, storage, access, and recovery paths separately. A cloud offering handling CUI also has applicable DFARS/FedRAMP obligations; “encrypted backup” alone does not resolve those obligations. References: NIST SP 800-171 Revision 2 and our CMMC External Service Provider guide.
A practical SSP classification review
- Trace CUI: identify processing, storage, transmission, temporary copies, and recovery paths. Evaluate CUI Asset treatment and applicable specialized provisions.
- Identify protection: record authentication, boundary enforcement, configuration, monitoring, and administrative dependencies. Evaluate SPA functions without overlooking CUI handling.
- Review intended use: capability combined with established policies, procedures, and practices prohibiting intended CUI use may support CRMA treatment. It remains in scope.
- Justify exclusions: verify separation, inability to handle the organization’s CUI, absence of a security protection role, and that no in-scope category applies. Sharing a network or being technically blocked does not, by itself, establish CRMA status.
For each component, record its owner, functions, data flows, classification rationale, applicable safeguards, and supporting evidence. Resolve systems with overlapping roles during scope planning. See the CRMA versus Out-of-Scope comparison above for boundary validation examples.
Separate VLANs and CMMC Level 2: what stays in scope?
A separate VLAN does not automatically make an asset out of scope. Classification depends on what information the asset handles, what security functions it provides, and whether separation actually prevents CUI handling. A device can be separated from the CUI network and still access CUI through cloud email, SharePoint, a VPN, or another transfer path.
CRMA means Contractor Risk Managed Asset. These assets can handle CUI but are not intended to do so under established security policies, procedures, and practices. CRMAs remain in scope; physical or logical separation from CUI Assets is not required. They receive different assessment treatment from CUI Assets.
| Asset or situation | Likely category | Why / what to verify |
|---|---|---|
| Backup server on a separate backup VLAN storing CUI backups | CUI Asset — in scope | Storing CUI keeps it in scope regardless of the VLAN. |
| Laptop on an office VLAN opening CUI in cloud email or SharePoint | CUI Asset — in scope | Cloud access still processes CUI. Blocking local server access does not block every CUI path. |
| Firewall on a management VLAN enforcing the CUI enclave boundary | Security Protection Asset — in scope | It protects the assessed environment even if it stores no CUI. |
| SIEM or security monitoring server on a separate security VLAN | Security Protection Asset — in scope, when providing protection without handling CUI | Its security role keeps it in scope. If collected content includes CUI, evaluate CUI handling as well. |
| General office workstation capable of receiving CUI, with established workflows prohibiting that use | Potential CRMA — in scope | Policies, procedures, and actual practices must support the classification. A policy statement alone does not establish out-of-scope status. |
| Qualifying production controller using CUI on an OT VLAN | Potential Specialized Asset — in scope | Verify that it meets the Specialized Asset definition and document its risk-based treatment. An OT VLAN alone does not qualify it. |
| Visitor device on internet-only guest Wi-Fi | Potential Out-of-Scope Asset | Verify separation, inability to handle the organization’s CUI, and absence of a security protection role. Check cloud access and remote access as well as local routing. |
| Printer on a separate printer VLAN receiving CUI print jobs | CUI handling — in scope; evaluate whether Specialized Asset treatment applies | A separate printer network does not remove the protected information it receives or prints. |
| Camera or access-control system on a separate security VLAN | Depends on its role | If it provides security protection for CUI Assets, evaluate it as a Security Protection Asset. If it handles no CUI and provides no such protection, evaluate the out-of-scope criteria. |
| Endpoint used only for a restricted VDI session | Conditional Out-of-Scope Asset exception | The rule recognizes an endpoint configured to allow no CUI processing, storage, or transmission beyond keyboard/video/mouse interaction. Verify the actual configuration; installing a VDI client is insufficient. |
These examples apply the Level 2 scoping rules to common situations; they are not automatic classifications for every implementation.
What becomes automatically out of scope on a separate VLAN?
Nothing solely because it is on a different VLAN. For the general Out-of-Scope Asset category, verify all of the following:
- The asset cannot process, store, or transmit the organization’s CUI.
- It does not provide security protection for CUI Assets.
- It is physically or logically separated from CUI Assets.
- It does not meet an in-scope asset category.
Review and test relevant firewall rules, inter-VLAN routing, identity permissions, cloud applications, VPN access, and file-transfer paths. Retain a practical explanation and validation results to support the boundary. A VLAN name or a “no CUI allowed” policy does not establish these conditions.
Which devices are always out of scope?
There is no blanket exemption by device type. Personal laptops, guest phones, cameras, printers, and production equipment must be evaluated by capability, use, security role, and separation. The restricted VDI endpoint provision above is an explicit conditional exception, not a general exemption for remote-access devices.
For the four in-scope categories, maintain the asset inventory, document asset treatment in the System Security Plan (SSP), and include the assets in the assessment-scope network diagram. In scope does not mean every category receives the same assessment treatment.
Official reference: 32 CFR 170.19(c), Table 3 — CMMC Level 2 asset categories and associated requirements. These examples address Level 2; Level 1 and Level 3 have different scoping rules.
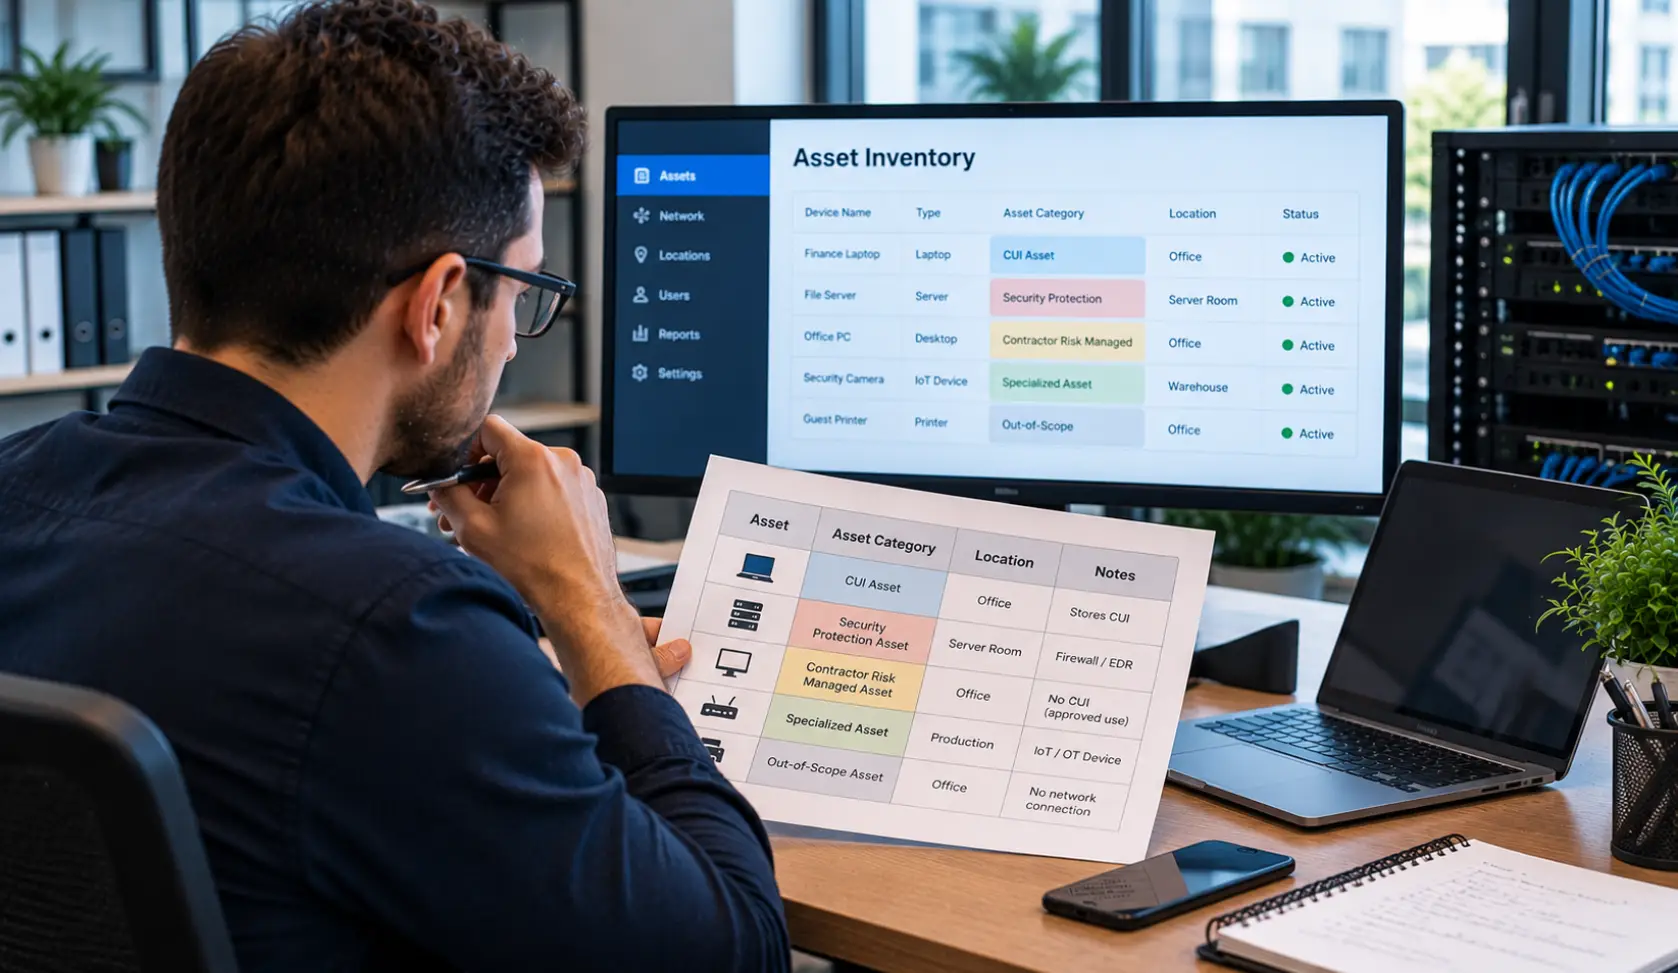
1. CUI Assets: where protected information travels
Illustrative example: An estimator opens a CUI drawing on a laptop, saves a copy to a project repository, and prints it. Investigate the laptop, repository, print path, and paper handling. Do not stop at the original file location.
A personal phone opening CUI email is not exempt because the employee owns it. An encrypted work container is a protection layer, not an automatic exemption for the underlying device. Read our BYOD guidance.
2. Security Protection Assets: what protects the environment
Illustrative example: A security service collects alerts from the company’s CUI workstations. Investigate its role even if its logs contain no CUI. Review security administrators and supporting services as well as appliances.
Security Protection Data can include configurations, vulnerability information, logs, and access credentials. “We only send logs to that provider” does not settle the scope question. For provider examples and assessment responsibilities, read our CMMC External Service Provider guide for MSPs and MSSPs.
3. Contractor Risk Managed Assets: capable, but not intended
Illustrative example: A general office workstation is technically capable of receiving CUI, but established workflows prohibit that use. It may qualify as a Contractor Risk Managed Asset rather than an Out-of-Scope Asset. Actual use and safeguards must support the classification.
This category is not permission to ignore the workstation. It remains in the inventory, scope diagram, and SSP treatment. Physical or logical separation from CUI Assets is not required for this category.
4. Specialized Assets: equipment with distinct constraints
Qualifying types include IoT/IIoT, Operational Technology, Government Furnished Equipment, Restricted Information Systems, and Test Equipment.
Illustrative example: A manufacturer should investigate a production controller using protected specifications. Determine whether it meets the Specialized Asset definition and how its risks are managed. An ordinary laptop does not become specialized simply because replacing or securing it is inconvenient.
5. Out-of-Scope Assets: a defensible separation
Illustrative example: A guest tablet on a separate network may be a candidate if it cannot reach or handle CUI and provides no security protection to the assessed environment. Verify account access, cloud services, and data-transfer paths as well as network rules.
A VLAN name or handbook statement alone does not demonstrate exclusion. The guide also has a narrow VDI endpoint exception for keyboard/video/mouse-only interaction; unrestricted downloads, clipboard transfers, or drive redirection require further review.
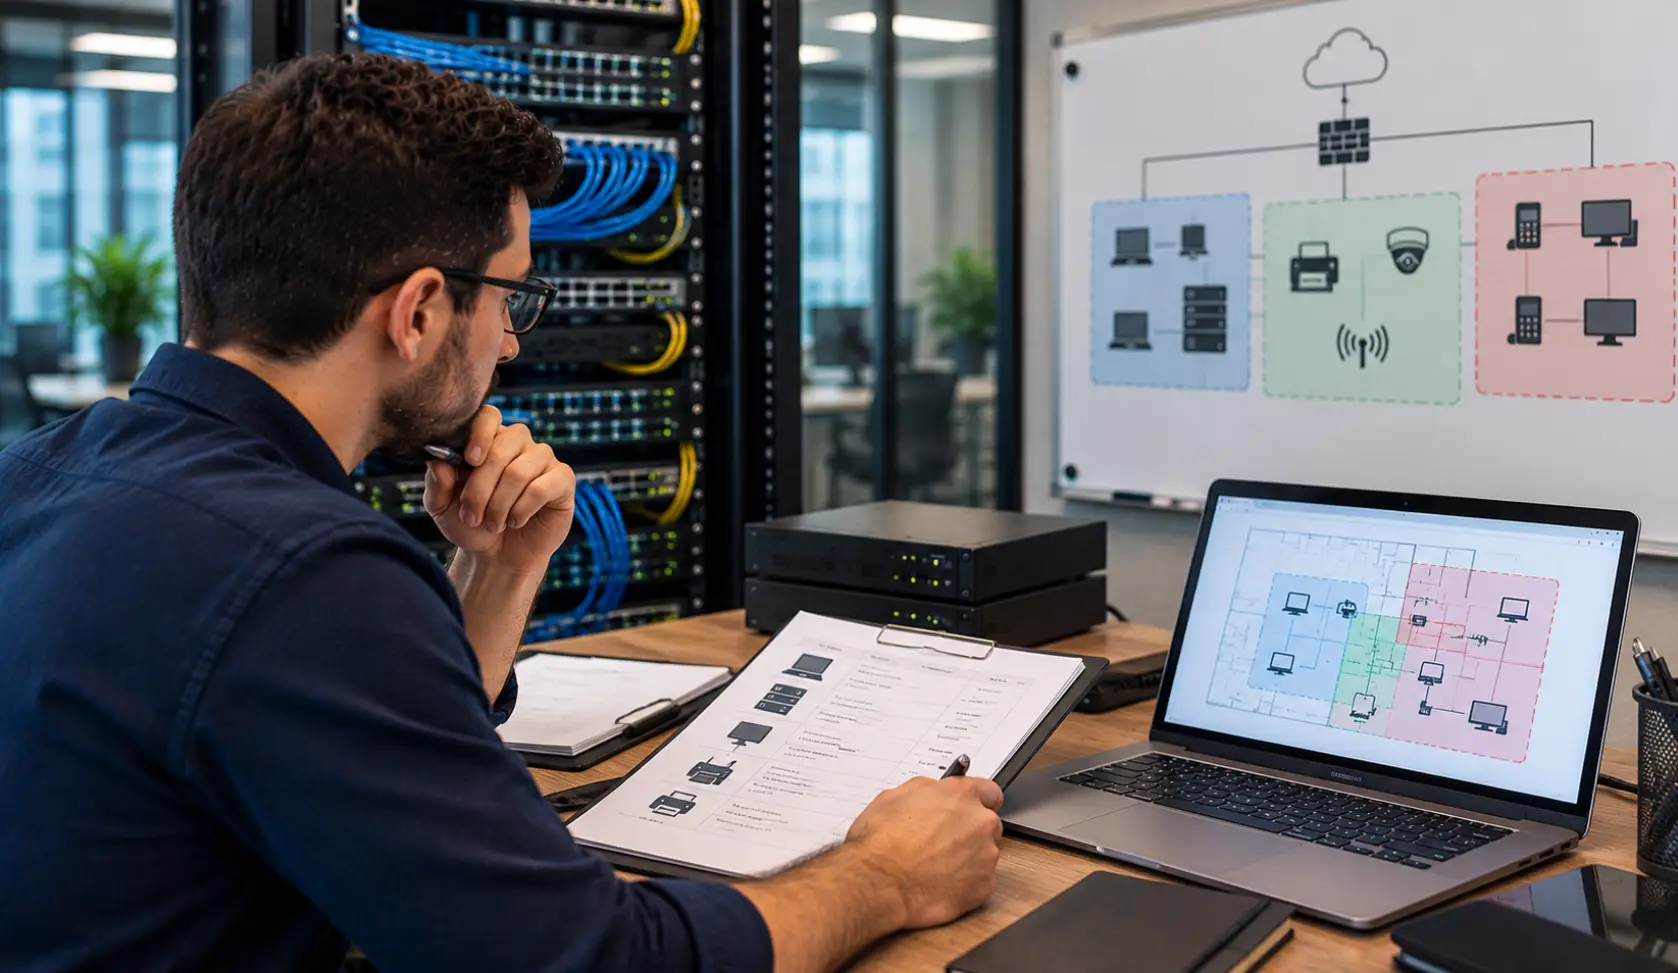
What should you document?
For the four in-scope categories, maintain an asset inventory, document treatment in the System Security Plan (SSP), and include the assets in the scope network diagram. Out-of-Scope Assets have no formal documentation requirement under this scoping guidance, but keeping a short explanation and validation results is useful practice.
These category details and assessment distinctions come from the DoD Level 2 Scoping Guide. Level 1 uses its own scoping guide.
A practical starting point for a small business
Walk through one contract workflow from receipt to disposal. List the people, devices, applications, storage, backups, print paths, and providers involved. For each candidate asset, record its owner, purpose, data handled, proposed category, and reason. Resolve uncertainty before finalizing the boundary.
Limit where protected information needs to go, then protect every part of that workflow. Keeping scope manageable starts with business decisions about access and handling.
Frequently Asked Questions
1. What are the five CMMC Level 2 asset categories?
The five categories are CUI Assets, Security Protection Assets, Contractor Risk Managed Assets, Specialized Assets, and Out-of-Scope Assets. Each category has a different role in determining assessment scope and documentation.
2. Are all five CMMC asset categories in scope?
No. The first four categories remain in scope under the Level 2 scoping model. Qualifying Out-of-Scope Assets are excluded when they meet the applicable criteria.
3. What is the difference between a CUI Asset and a Security Protection Asset?
A CUI Asset processes, stores, or transmits Controlled Unclassified Information. A Security Protection Asset provides security functions for the assessment scope. An asset’s role, rather than its name alone, determines its classification.
4. Can a regular office computer be a Contractor Risk Managed Asset?
Potentially. The computer must be capable of handling CUI, while established policies, procedures, and practices demonstrate that it is not intended to do so. The classification must be supported by actual workflows and safeguards.
5. What qualifies as a Specialized Asset under CMMC?
Qualifying examples can include IoT and industrial IoT devices, operational technology, government-furnished equipment, restricted information systems, and test equipment. The asset must meet the applicable definition; difficulty securing an ordinary device does not automatically make it specialized.
6. How can a business justify an Out-of-Scope Asset?
The business should verify that the asset cannot handle CUI, does not provide security protection for CUI Assets, and is appropriately separated from the assessed environment. Network rules, account permissions, cloud access, and data-transfer paths may all need review.
7. What documentation should a business maintain for CMMC asset categories?
For the four in-scope categories, the scoping guidance calls for an asset inventory, treatment in the System Security Plan (SSP), and inclusion in the scope network diagram. Keeping supporting notes and validation results for exclusions is also useful practice.
Need help organizing your CMMC scope?
Business Communication Solutions helps businesses map information flows, review asset classifications, and plan practical safeguards. Explore our CMMC consulting services.
Austin: 512-257-1433
Houston: 281-815-8784
Lampasas: 512-865-4000