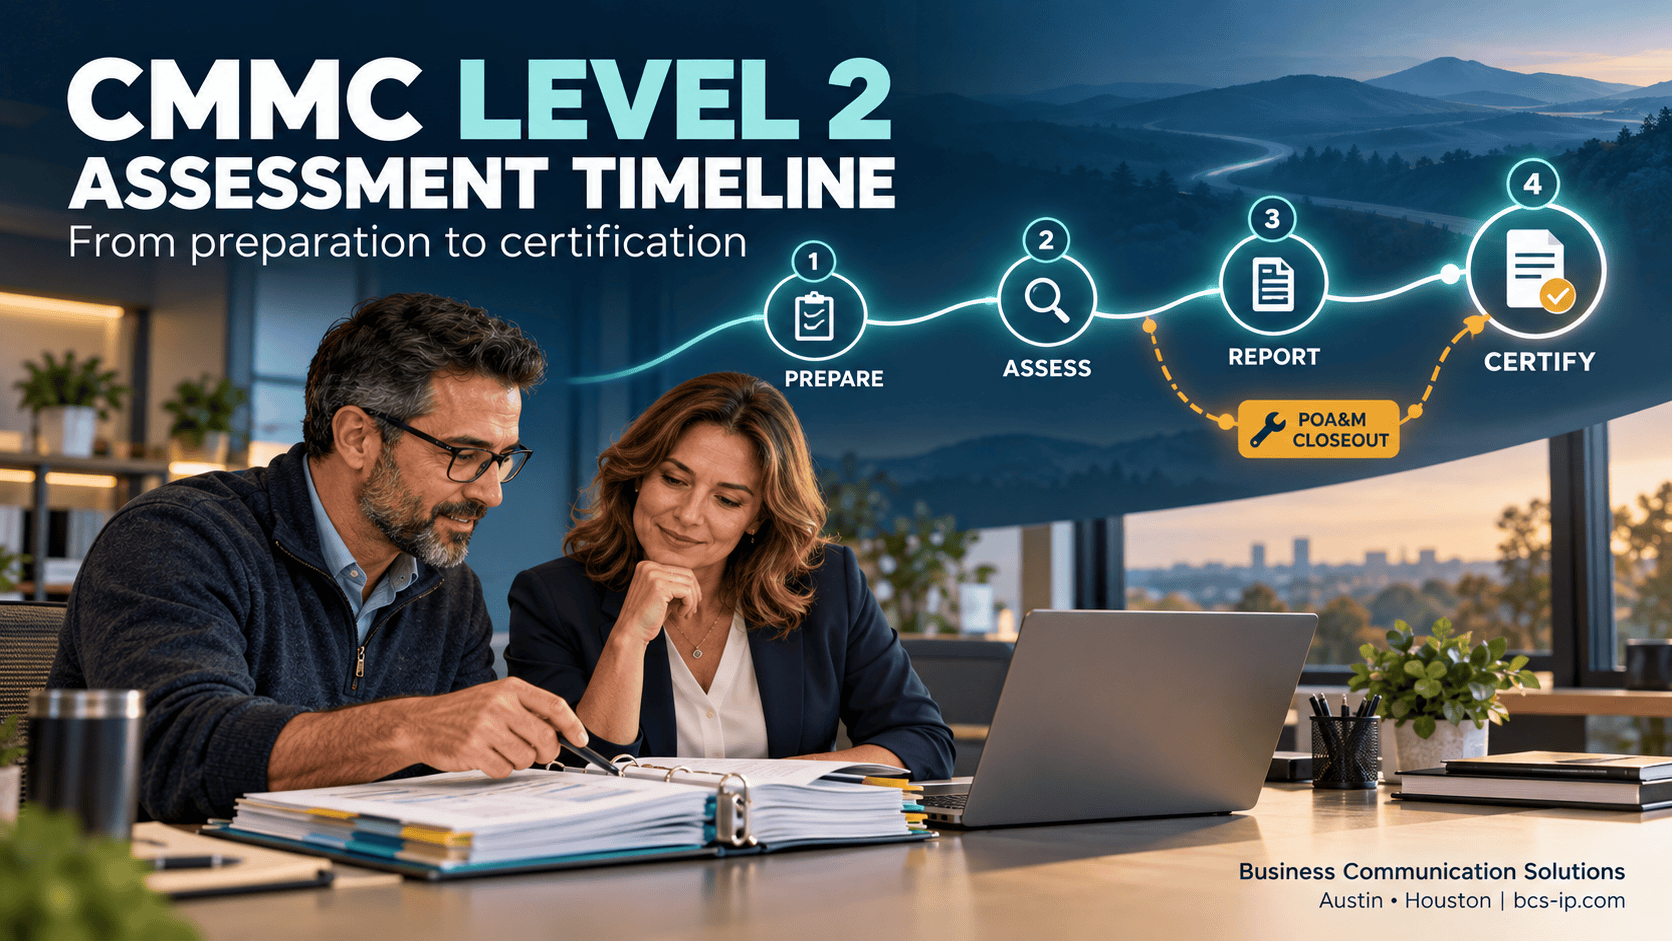
What happens after you contact a C3PAO? This CMMC Level 2 assessment timeline follows your business from the first conversation through the four CAP phases, findings, possible POA&M closeout, and Final Level 2 (C3PAO) status.
Business Communication Solutions helps Austin and Houston contractors prepare their systems, documentation, and evidence for an independent assessment. Austin: 512-257-1433 · Houston: 281-815-8784.
How to use this guide: “Beginning, middle, and end” are our explanatory checkpoints, not official CAP subphases. The phase sequence follows the Cyber AB’s CAP v2.0. Preparation examples below are BCS recommendations. These assessment phases are separate from the government’s CMMC contract rollout phases. Confirm whether your contract requires Level 2 self-assessment or a C3PAO certification assessment.
Jump to: First contact · Phase 1 · Phase 2 · Re-evaluation · Phase 3 · Phase 4 · POA&M rules · After certification
How many days does a C3PAO have to respond to an OSC?
Current CAP v2.0: Its preliminary proceedings do not specify a fixed number of days for the C3PAO’s first reply to an Organization Seeking Certification (OSC). Agree on communication expectations when requesting a quote.
Why you may have heard “five business days”: The 2022 pre-decisional draft, section 1.1, recommended that response timeframe. It used “should,” and the wording is not carried into the currently published CAP v2.0. Treat it as historical guidance rather than a current mandatory deadline.
BCS recommendation: Ask for acknowledgment within five business days as a commercial communication target. If you receive no response, follow up and compare other eligible C3PAOs. Request a written schedule covering the coordination call, quote, document delivery, assessment dates, reporting, and any closeout availability.
CMMC assessment timing: Required clocks and agreed schedules
Use this table with the phase-by-phase walkthrough below. Business days and calendar days are different. Record each triggering event and obtain the actual due date from your C3PAO. A report-delivery condition can end re-evaluation eligibility before the full ten-business-day period.
| Milestone | Timing | What the OSC should know |
|---|---|---|
| Initial request from the OSC | No fixed initial-reply deadline in CAP v2.0 | Agree on a response target with the C3PAO. An acknowledgment does not reserve assessment dates. |
| Older five-business-day response guidance | Historical recommendation | The 2022 draft recommended acknowledgment and coordination within five business days; this wording is absent from v2.0. |
| Contract, scope discussion, and Phase 1 preparation | Schedule agreed with the C3PAO | Ask for document due dates and a readiness decision date. Avoid treating this as a guaranteed number of days. |
| Phase 2 active assessment | Duration agreed for the engagement | Reserve staff and provider availability for the full assessment schedule. |
| Security requirement re-evaluation | During assessment and up to 10 business days after active assessment | Only if the conditions in 32 CFR 170.17(c)(2) are met and the Findings Report has not been delivered. |
| Phase 3 quality review and results submission | Confirm the engagement schedule | Ask when to expect the out-brief, report, and eMASS submission; do not assume all three happen on the last fieldwork day. |
| Initial appeal to the C3PAO | Its published, time-bound appeals process | Get the policy and filing deadline before you need them. |
| Escalating an appeal to the Cyber AB | Within 15 business days of receiving the C3PAO’s written appeal decision | CAP v2.0, section 3.28. This clock begins with the appeal decision, not the assessment out-brief. |
| Certificate issuance | Follows eMASS status confirmation | Ask for an issuance target. It is separate from the last day of interviews. |
| Conditional status POA&M closeout | Within 180 calendar days of the Conditional CMMC Status Date | Complete remediation, C3PAO closeout, and posting of compliance results within this period. |
| Affirmation in SPRS | After each assessment, including closeout, and annually thereafter | Assign the Affirming Official and calendar reminders. See 32 CFR 170.22. |
| Next Level 2 certification assessment | Within the applicable three-year cycle | Successful POA&M closeout does not reset the original CMMC Status Date. |
| Assessment evidence retention | Six years from the CMMC Status Date | Retain the hashed evidence artifacts and integrity records required by 32 CFR 170.17(c)(4). |
Timing references: CAP v2.0, preliminary proceedings and sections 3.23–3.28; 32 CFR 170.17; 170.21; 170.22; and 170.4.
Before Phase 1: Contacting and engaging a C3PAO
Beginning: Identify an authorized or accredited C3PAO and describe the legal entity, systems, locations, CAGE codes, and assessment you need. Ask about availability, evidence handling, pricing, and the assessment and appeals processes. Read our consultant vs. C3PAO guide before selecting an assessor.
Middle: Disclose prior consulting and relevant relationships for conflict review. Discuss the proposed boundary, provider participation, onsite needs, and staff availability. Recommend naming one business coordinator, an IT lead, and the senior official responsible for affirmations.
End: Complete the engagement agreement and confidentiality arrangements. Build a shared preparation schedule with named owners. Booking an assessment does not establish readiness or guarantee a successful result.
Phase 1: Pre-assessment and readiness
Beginning: The C3PAO reviews the System Security Plan (SSP) and validates the assessment scope. Use our scoping guide and five asset categories guide to prepare a consistent inventory, boundary diagram, and explanation of how CUI moves.
Middle: Evidence and personnel availability are checked, including relevant providers. Scope disagreements must be resolved before Phase 2. Readiness here means the assessment can proceed; it is not a preliminary passing grade.
End: Planning information receives quality review and the pre-assessment form is uploaded into CMMC eMASS. If readiness is inadequate, the assessment can be postponed or canceled. Avoid treating a scheduled start date as a reason to rush into an assessment your team cannot support.
What your business should have ready
BCS preparation checklist: Current SSP; asset inventory and category rationale; network and CUI-flow diagrams; evidence index mapped to objectives; approved policies; user and administrator lists; facility access information; and provider contacts. For outsourced responsibilities, gather service descriptions and customer responsibility matrices using our ESP guide.
Small-shop example: For a file server and backup NAS in a locked room, organize the actual user permissions, administrator authorizations, backup configuration, room access records, and network diagram. Explain how confidentiality is protected instead of relying on the statement “the NAS requires MFA.” Our FIPS encryption guide helps your team prepare that discussion.
Phase 2: Assessing the implemented security requirements
Beginning: An opening meeting establishes how the assessment will run. Recommend confirming who can demonstrate each system, where records are located, and how requests will be tracked. Give subject-matter experts time to participate rather than routing every question through one administrator.
Middle: Assessors examine records, interview personnel, and test implementation. Evidence should show how the controls actually operate. The scoring rule requires all applicable objectives to be satisfied for a MET finding, using final evidence rather than draft or unapproved policies.
End: Checkpoint discussions surface findings and unresolved evidence requests as active evaluation concludes. Ask which objectives remain unsupported and what evidence is needed. Track the reason for each potential NOT MET finding; a product purchase or a policy title alone does not establish that its objectives are satisfied.
Checkpoint: Evidence gaps should surface during the assessment
Before active assessment: Phase 1 checks scope and evidence availability. During Phase 2, the assessors evaluate whether the implementation and evidence satisfy the objectives. Having a policy file available is different from demonstrating that the policy is approved, implemented, and supported by operating records.
When a gap is identified: Record the specific objective, missing evidence, responsible person, and assessor-confirmed cutoff. Use the re-evaluation conditions described below for the short assessment window. Eligible unresolved requirements follow the separate certification POA&M rules; the two processes have different triggers and deadlines.
How to manage evidence requests
BCS recommendation: Keep a request log with the requirement/objective, requested record or demonstration, owner, due time, and submitted version. For an access-control demonstration, show an authorized user accessing permitted CUI and an unauthorized user being denied, then provide the related permissions and administrative process. That demonstration supports specific objectives; it does not prove the entire environment compliant.
“Limited deficiency”: The short re-evaluation window
If you hear “limited deficiency,” ask the assessor which current provision they mean. For this timeline, the relevant rule is security requirement re-evaluation under 32 CFR 170.17(c)(2). It permits re-evaluation during the assessment and for 10 business days after the active assessment period, when all three conditions are satisfied:
1. Additional evidence demonstrates the requirement is MET.
2. The change cannot reduce or limit the effectiveness of other requirements already scored MET.
3. The Assessment Findings Report has not been delivered.
Practical handling: Raise missing evidence promptly and confirm the assessor’s cutoff. For example, your team may locate a completed, approved record that was not initially supplied. Do not budget this window as an automatic extension for unfinished implementation, or assume every finding is eligible.
A separate concept: An operational temporary deficiency in a previously implemented control is different from a certification POA&M. Its treatment depends on the definitions and conditions in 170.4 and 170.24. An unfinished implementation cannot simply be renamed a temporary deficiency.
Phase 3: Completing and reporting results
Beginning: The assessment team assembles the findings, supporting rationale, scores, and recommended outcome. Recommend checking that the identified information system and associated business identifiers match the agreed scope.
Middle: An independent quality reviewer checks the assessment work. Use the C3PAO’s review and appeals procedures for disputed findings. Prepare objective-specific evidence and a clear explanation rather than relying on a general statement that your environment is secure.
End: The out-brief communicates the results, followed by the required submission into CMMC eMASS. Results flow to SPRS. Confirm the report, recorded outcome, and any eligible POA&M items with your C3PAO. A positive conversation during fieldwork is not the issued certificate.
Checkpoint: Independent quality review comes before final reporting
The C3PAO’s quality assurance reviewer must be a CMMC-Certified Assessor (CCA) who was not on this assessment team. The OSC’s compliance officer can coordinate the business’s evidence but does not perform this independent C3PAO quality function. Older material may call the role a CQAP. See 32 CFR 170.9(b)(13).
Practical sequence: Finish the evaluative work and any permitted re-evaluation; compile findings and scores; complete independent quality review; hold the out-brief; upload the results; then issue the applicable certificate after status confirmation. Ask your C3PAO to put the report, upload, and issuance targets on the engagement schedule.
Where the older 20-day and five-day timelines fit
The 2022 pre-decisional draft used a different sequence and terminology. It specified quality-review submission within 10 business days and eMASS upload within 20 business days of the Final Findings Briefing.
That draft also described limited-deficiency corrections within five business days of that briefing, or an assessor-set alternative no later than five calendar days before report submission to eMASS. These are historical draft provisions, not the current timeline used in this guide.
For current scheduling, use the conditional 10-business-day re-evaluation window under 170.17(c)(2). CAP v2.0 section 3.17 directs uploads under current eMASS procedures; it does not repeat the old 20-business-day rule. Confirm applicable reporting procedures and dates with the C3PAO.
What the outcome means
Final Level 2 (C3PAO): All requirements are satisfied under the scoring methodology, resulting in the full 110-point score. Properly justified N/A objectives receive equivalent MET treatment.
Conditional Level 2 (C3PAO): The score is at least 88 and every remaining NOT MET item meets the POA&M restrictions.
No Conditional or Final status: The result is below the threshold or includes an unmet requirement that cannot be placed on the certification POA&M. A score of 88 alone is insufficient.
Decision checkpoint: 85, 88, or 92 points
85/110 when results are finalized: Below the 88-point Conditional threshold. The OSC does not achieve Conditional or Final status. Remediate and arrange the required reassessment; there is no automatic five-day extension based on this score.
88/110: Potentially eligible for Conditional status only when every remaining NOT MET requirement qualifies for the certification POA&M. The score alone does not grant a correction window. Once Conditional status is recorded, the 180-calendar-day clock runs from its CMMC Status Date.
92/110 with an unsupported one-point requirement: That requirement remains NOT MET. It may be included in the certification POA&M only if it is eligible and all other conditions are satisfied. Some one-point requirements are specifically prohibited from POA&Ms. It neither automatically fails the entire assessment nor automatically qualifies for deferral.
These are weighted assessment scores, not a count of how many requirements were checked off. Apply 170.21 POA&M restrictions alongside the scoring methodology.
Checkpoint: Reserve closeout time before the deadline
Phase 4: The C3PAO verifies the eligible POA&M requirements through the closeout assessment. The OSC and its implementation providers do the remediation work. Recommend setting an internal completion date well ahead of day 180 so evidence review, assessment, and required results posting can finish on time.
Phase 4: Certificate issuance and any POA&M closeout
Beginning: Once the status is confirmed through eMASS, the C3PAO prepares and issues the applicable Conditional or Final certificate. Check its scope, identifiers, and CMMC Status Date.
Middle — Final route: If the initial assessment achieved Final status, there is no certification POA&M closeout to perform. Move into ongoing control operation, evidence retention, and affirmation management.
Middle — Conditional route: Assign remediation owners, implement the corrections, and arrange a C3PAO closeout assessment early. The closeout evaluates the eligible requirements left NOT MET in the initial assessment. Send evidence with enough time for review, assessment, and required results submission.
End: Successful closeout produces Final status. Remediation, the C3PAO closeout assessment, and posting compliance results must occur within 180 days of the Conditional CMMC Status Date. Conditional status expires if that deadline is missed. Finishing the technical fix on day 180 is too late if assessment and posting remain outstanding.
POA&M eligibility: What can remain open?
A readiness task list can include any work your business needs to finish. A certification POA&M is restricted by 32 CFR 170.21. Level 2 requires at least 88 points. Generally, remaining items must be one-point requirements. The specific exception is CUI encryption requirement 3.13.11 when encryption is used but is not FIPS-validated, carrying the specified three-point deduction.
These six requirements cannot be left on that POA&M: 3.1.20 external connections; 3.1.22 control of public information; 3.12.4 SSP; 3.10.3 escorting visitors; 3.10.4 physical access logs; and 3.10.5 managing physical access. Use the exact requirement and objective findings with your assessor when determining eligibility.
See why 88 vs. 87 matters and how backup encryption affects the result for a worked example. Do not assume every encryption shortcoming qualifies for the narrow FIPS exception.
The dates to put on your calendar
Active assessment end: Track the potential 10-business-day re-evaluation window and the earlier report-delivery limit.
Conditional CMMC Status Date: Starts the 180-day remediation, closeout, and results-posting deadline. Under the Status Date definition, this is tied to results submission—not the first call, first interview, or certificate email.
Successful closeout: Does not restart the original Status Date or create a fresh three-year certification period.
BCS scheduling recommendation: Work backward from your contract need. Reserve time for readiness fixes before Phase 1, staff participation during Phase 2, report review, and any permitted closeout. Assessment size, locations, provider coordination, and C3PAO availability affect elapsed time. The four phases do not each have a universal fixed number of days.
After Final Level 2: Keep the status current
Your Affirming Official must submit the required affirmation in SPRS after each assessment, including POA&M closeout, and annually thereafter. 32 CFR 170.22 explains the official’s authority and the continuing-compliance statement. Recommend assigning calendar ownership and a backup contact.
Plan the next certification assessment within the applicable three-year cycle and maintain the assessed controls between assessments. Retain the hashed assessment artifacts for six years from the CMMC Status Date as required by 170.17(c)(4). Keep the artifact-name list, hashes, and hashing algorithm available; preserve the evidence versions used for the assessment.
CMMC readiness support in Austin and Houston
BCS helps small contractors organize scope, improve technical controls, coordinate provider evidence, and prepare for independent assessment. Our Austin and Houston CMMC consulting services connect the readiness plan with the systems your team operates. BCS provides readiness and implementation support; the authorized or accredited C3PAO performs the certification assessment.
Talk through your next step: Austin 512-257-1433 · Houston 281-815-8784.
Sources and review date
Reviewed October 26, 2026. Phase structure: Cyber AB downloads — CMMC Assessment Process v2.0. Requirements: C3PAO responsibilities (170.9); Level 2 certification (170.17); POA&Ms (170.21); affirmations (170.22); scoring (170.24); definitions (170.4). Confirm the current requirements and assessment arrangements with your C3PAO.