Every device, account, and piece of software your business uses is a potential door into your network. The more doors you have, and the less you know about where they all are, the easier it is for someone to slip through one you forgot was open. That collection of doors is what security professionals call your “attack surface,” and for most small businesses, it is bigger than they think.
What Is an Attack Surface?
Your attack surface is every system, account, device, and piece of software that a cybercriminal could potentially use to get into your business. That includes obvious things like your computers and servers, but also email accounts, cloud apps, old employee logins that were never disabled, personal devices connecting to your Wi-Fi, and even smart devices like cameras or thermostats. Every one of these is a possible entry point, and most businesses have far more of them than anyone has actually counted.
Types of Security Exposure
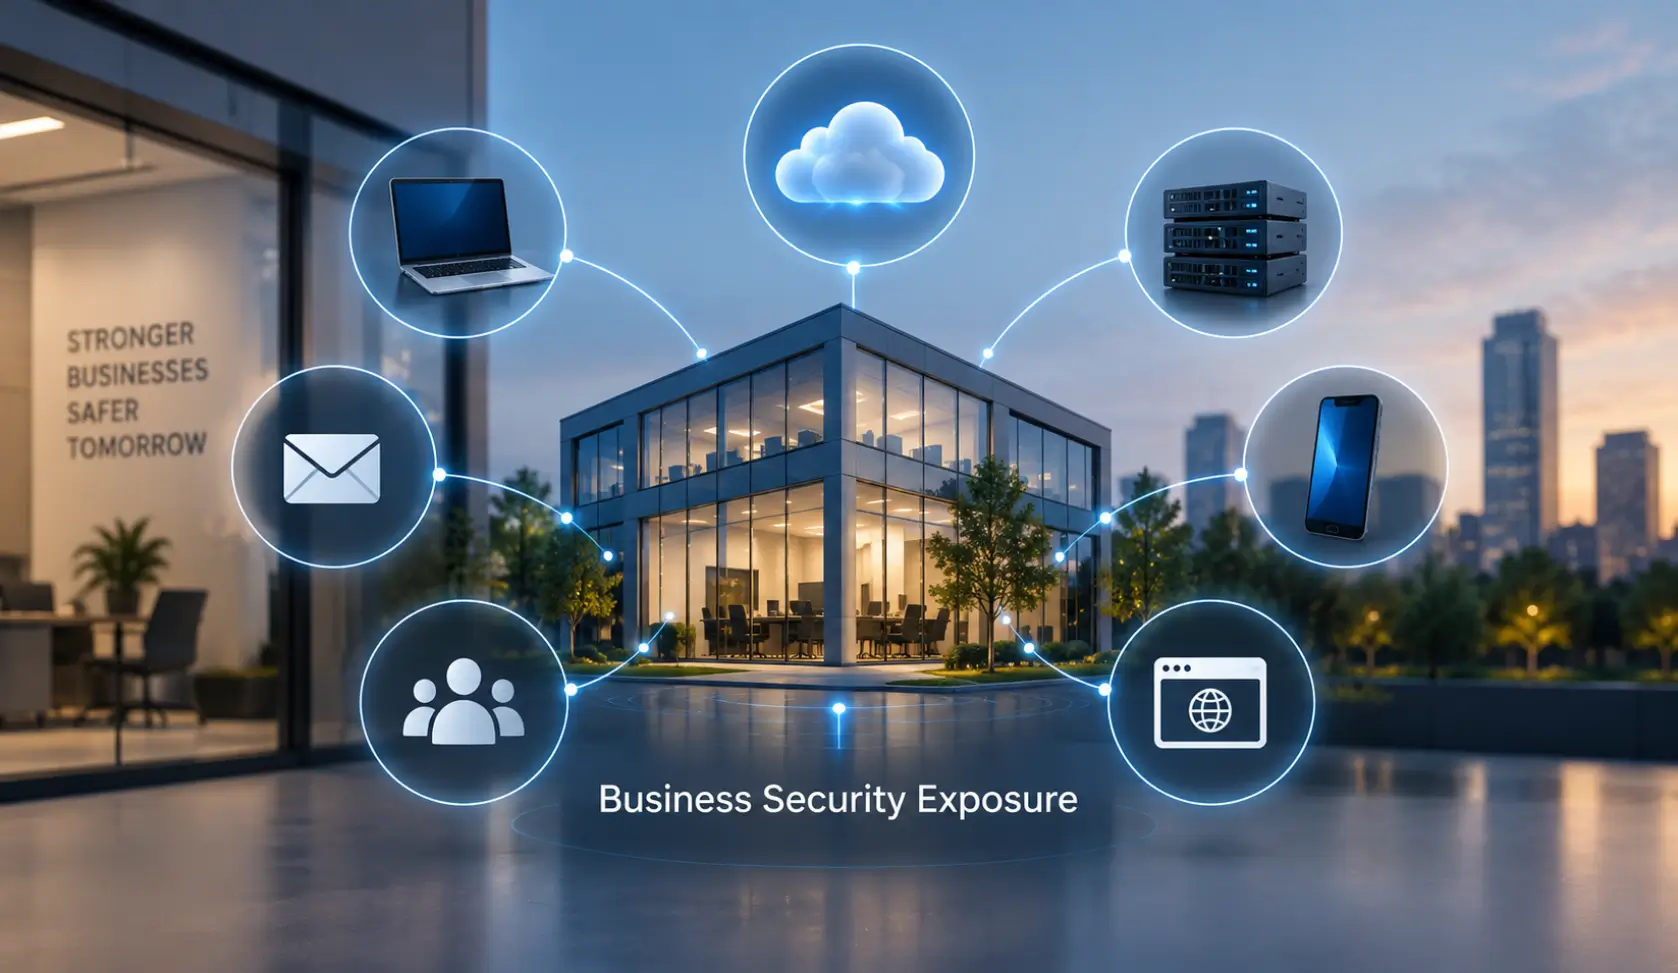
A business can have several areas that require protection. These may include technology, user accounts, networks, cloud applications, and devices connected to the business environment.
Digital Exposure
Websites, cloud applications, email accounts, remote access services, and internet-facing systems can create potential entry points for attackers.
Network Exposure
Routers, firewalls, wireless networks, servers, and remote connections can introduce risk when they are unnecessarily accessible or incorrectly configured.
Endpoint Exposure
Laptops, desktops, mobile devices, and other endpoints can become vulnerable when they use outdated software, weak configurations, or unauthorized applications.
Human and Account Exposure
User accounts can create security risks through weak passwords, excessive permissions, phishing attacks, or accounts that remain active after an employee leaves.
Cloud and SaaS Exposure
Cloud platforms and business applications can introduce additional accounts, permissions, integrations, and data-access points that need to be monitored and secured.
Understanding these different areas helps businesses identify unnecessary exposure and prioritize the security controls they need.
Why It Matters for Small Businesses in Austin
Attackers do not need to target your business specifically to find a way in. Automated tools scan the internet around the clock looking for exposed logins, outdated software, and unsecured devices, then flag whatever they find for someone to exploit later. A small business with a sprawling, unmonitored attack surface looks exactly like an easy target to those tools, regardless of size or industry.
How Your Attack Surface Grows Without You Noticing
Attack surfaces rarely grow on purpose. A new SaaS tool gets signed up for and forgotten. An employee leaves, but their account stays active. A laptop gets replaced, but the old one is still logged into company email. A router or camera keeps running its factory-default password years after installation. None of these decisions feel risky in the moment, but together they add up to a much larger exposure than most business owners realize.
Unmonitored switches and legacy router configurations create open backdoors, underscoring the necessity of regular network security and firewall inspections.
Common Sources of Business Exposure
Security exposure can develop from everyday technology changes. Some common sources include:
- Unused employee accounts that remain active
- Outdated operating systems and applications
- Unnecessary internet-facing services
- Remote access with weak security controls
- Unmanaged computers and mobile devices
- Cloud accounts with excessive permissions
- Unused software and third-party integrations
- Default or weak passwords on connected devices
- Applications installed without proper security review
- Unsupported devices that no longer receive security updates
These issues can be difficult to identify when a business does not maintain an accurate inventory of its technology and user access. Regular reviews can help uncover systems or accounts that no longer have a legitimate business purpose.
How to Reduce Your Attack Surface
Reducing your attack surface comes down to knowing what you have and removing what you do not need. That means keeping an accurate inventory of devices, accounts, and software; disabling accounts and access as soon as someone leaves or a tool is no longer used; requiring multi-factor authentication (MFA) everywhere it is available; keeping systems patched and updated; and segmenting your network so a compromised device cannot reach everything else. None of these steps are exotic, but doing them consistently is what separates a business that is hard to breach from one that is not.
The single most effective barrier against unauthorized external access is enforcing SSL VPN and multi-factor authentication (MFA) on every remote portal.
A Practical Approach to Reducing Security Exposure
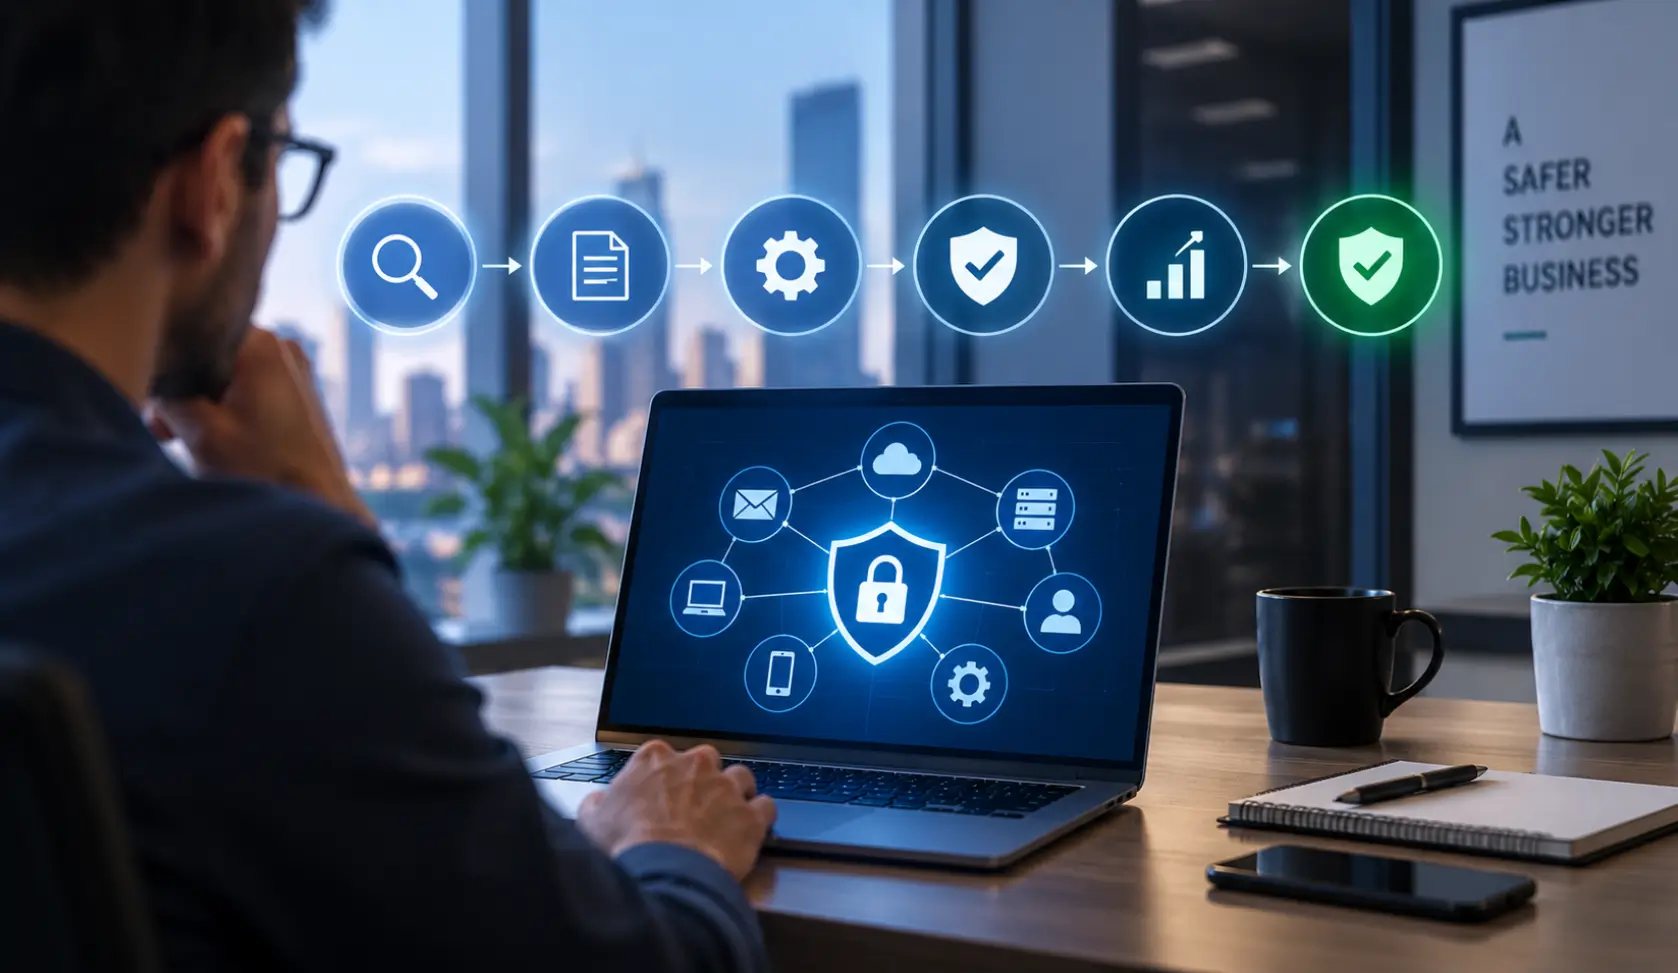
Reducing unnecessary exposure starts with knowing what exists in the business environment. A practical process can include the following steps:
- Create an asset inventory: Identify computers, mobile devices, servers, network equipment, applications, cloud services, and other connected systems.
- Review accounts and permissions: Look for inactive accounts, unnecessary administrator privileges, and users with access they no longer require.
- Identify internet-facing systems: Determine which services and remote-access points are accessible from outside the organization and whether they are necessary.
- Address outdated technology: Prioritize devices and applications that no longer receive security updates or have known vulnerabilities.
- Remove unnecessary access: Disable unused accounts, retire obsolete systems, close unnecessary services, and remove applications that are no longer required.
- Apply appropriate controls: Use measures such as multifactor authentication, patch management, endpoint protection, network segmentation, and least-privilege access.
- Review the environment regularly: New employees, applications, devices, and cloud services can change a company’s security exposure. Regular reviews help keep security controls aligned with the current environment.
This should be treated as an ongoing security process rather than a one-time cleanup exercise.
Segmenting internal traffic to contain potential lateral movement requires proper network switch and VLAN configuration across your office switches.
Security Tools That Support Risk Reduction
Different cybersecurity controls address different types of exposure. Businesses may use several layers of protection depending on their technology environment and security requirements.
- Multifactor authentication (MFA): Adds another verification step when users sign in to protected accounts.
- Endpoint security: Helps monitor and protect computers and other connected devices.
- Vulnerability management: Helps identify weaknesses that require remediation.
- Network segmentation: Separates parts of a network to help limit unauthorized movement between systems.
- SIEM: Collects and analyzes security information from multiple sources to help identify suspicious activity.
- Security monitoring: Helps detect unusual activity that may require further investigation.
These controls work together. No single technology eliminates security risk, so businesses should consider how their tools, users, devices, and access policies fit together.
Frequently Asked Questions
Q: What does ‘attack surface’ mean in cybersecurity?
A: An attack surface is the total sum of all potential points—such as hardware, software, accounts, open network ports, and human employees—where an unauthorized user can attempt to enter or extract data from your environment.
Q: What is the difference between a vulnerability and an attack surface?
A: An attack surface is the entire perimeter of entry points into your network, whereas a vulnerability is a specific flaw or weakness within one of those points that an attacker can exploit.
Q: What is Shadow IT, and why is it dangerous?
A: Shadow IT refers to applications, cloud software, or personal devices used by employees for work without the IT department’s knowledge or approval. Because these tools lack central security management, they leave undetected gaps in your perimeter.
Q: How does Multi-Factor Authentication (MFA) reduce attack surface?
A: MFA invalidates stolen password attacks. Even if a cybercriminal obtains an employee’s credentials via a phishing email, they cannot access the account without the secondary authentication factor.
Q: What is network segmentation?
A: Network segmentation is the practice of splitting a network into smaller, isolated subnetworks (VLANs). It prevents attackers who compromise a low-security device (like an office printer) from reaching critical servers or accounting databases.
Q: Why is offboarding employees important for security?
A: Orphaned accounts of former staff are prime targets for cybercriminals. Failing to revoke account access immediately upon departure leaves persistent doorways open into your systems.
Q: How often should an Austin business perform an attack surface scan?
A: Businesses should perform automated vulnerability scans at least monthly, supplemented by a comprehensive external network penetration assessment annually or following major infrastructure changes.
Q: Can physical security impact a digital attack surface?
A: Yes. Unsecured server rooms, open network jacks in waiting areas, and discarded un-shredded hard drives represent physical attack vectors that can lead to digital compromise.
How Business Communication Solutions Can Help
BCS helps Austin small businesses map out their full attack surface, close the gaps that get left open, and keep it that way with ongoing monitoring, MFA enforcement, patch management, and layered security across your network, endpoints, and cloud accounts. Reducing your attack surface is one part of a complete cybersecurity plan alongside SIEM, EDR, and 24/7 monitoring through our Security Operations Center (SOC).
BCS keeps your attack perimeter locked down through continuous log correlation with our managed SIEM monitoring services.
Want to see how attack surface reduction fits into a complete cybersecurity plan for your business? Visit our cybersecurity services page to learn more, or contact us today.
Call us now at 512-257-1433 or visit us at bcs-ip.com to schedule a free cybersecurity risk assessment.
Related Cybersecurity Reads:
- What Is SIEM? How It Helps Protect Your Business From Cyber Threats
- What Is SOAR? How It Helps Austin Small Businesses Respond Faster
- What Is a Firewall? A Simple Explanation for Businesses in Austin, TX
- Is Your Business Network Secure? 12 Warning Signs You Need Professional Services
- Cybersecurity for Austin Small Businesses Is a Team Effort