Are your business computers and servers protected against ransomware, malware and suspicious activity? Traditional antivirus may not catch every threat. BCS-IP helps protect your endpoints with managed EDR services that detect and respond to potential threats.
Managed EDR services help protect your business computers and servers by detecting suspicious activity, investigating potential threats and responding before they spread.
Our EDR endpoint protection services help Austin and Houston businesses strengthen device security, move beyond traditional antivirus and respond to threats before they disrupt daily operations.
Businesses looking for broader protection can also explore our cybersecurity services in Austin, covering additional security needs beyond endpoint protection.
What if an employee clicks a harmful link or ransomware starts running on an office computer? Our managed EDR services help catch suspicious activity early and protect your business devices before the problem spreads.
Understanding how endpoint detection fits into a wider security strategy can also help; read our guide to cybersecurity monitoring tools to learn how EDR, MDR, SIEM and other technologies work together.
01
02
03
04
Detect malicious files and ransomware activity on business devices.
Spot unknown applications and unusual processes running on endpoints.
Identify unexpected changes to files, settings or system behaviour.
Detect signs that a laptop or server may be infected.
Flag unusual actions that could point to a compromised account or device.
Identify related endpoint activity that may indicate a wider security issue.
An employee opens a suspicious attachment. A laptop starts acting strangely. Would you know what’s happening? Our managed EDR services help spot unusual device activity, investigate threats and protect other business devices…
Move beyond basic antivirus with EDR that detects suspicious behaviour and potential threats on business devices.
Spot suspicious file changes and ransomware-like activity that could put business data at risk.
Investigate suspicious device behaviour to understand whether malware or another threat is involved.
Get better visibility into endpoint activity and identify devices that need security attention.
Detect unusual activity after someone downloads or opens a potentially harmful attachment.
Identify unusual applications, processes and activities that may indicate a security threat.
Identify related suspicious activity across endpoints before a threat causes wider disruption.
Get managed EDR support to monitor endpoint threats and investigate suspicious activity without relying entirely on your in-house team.
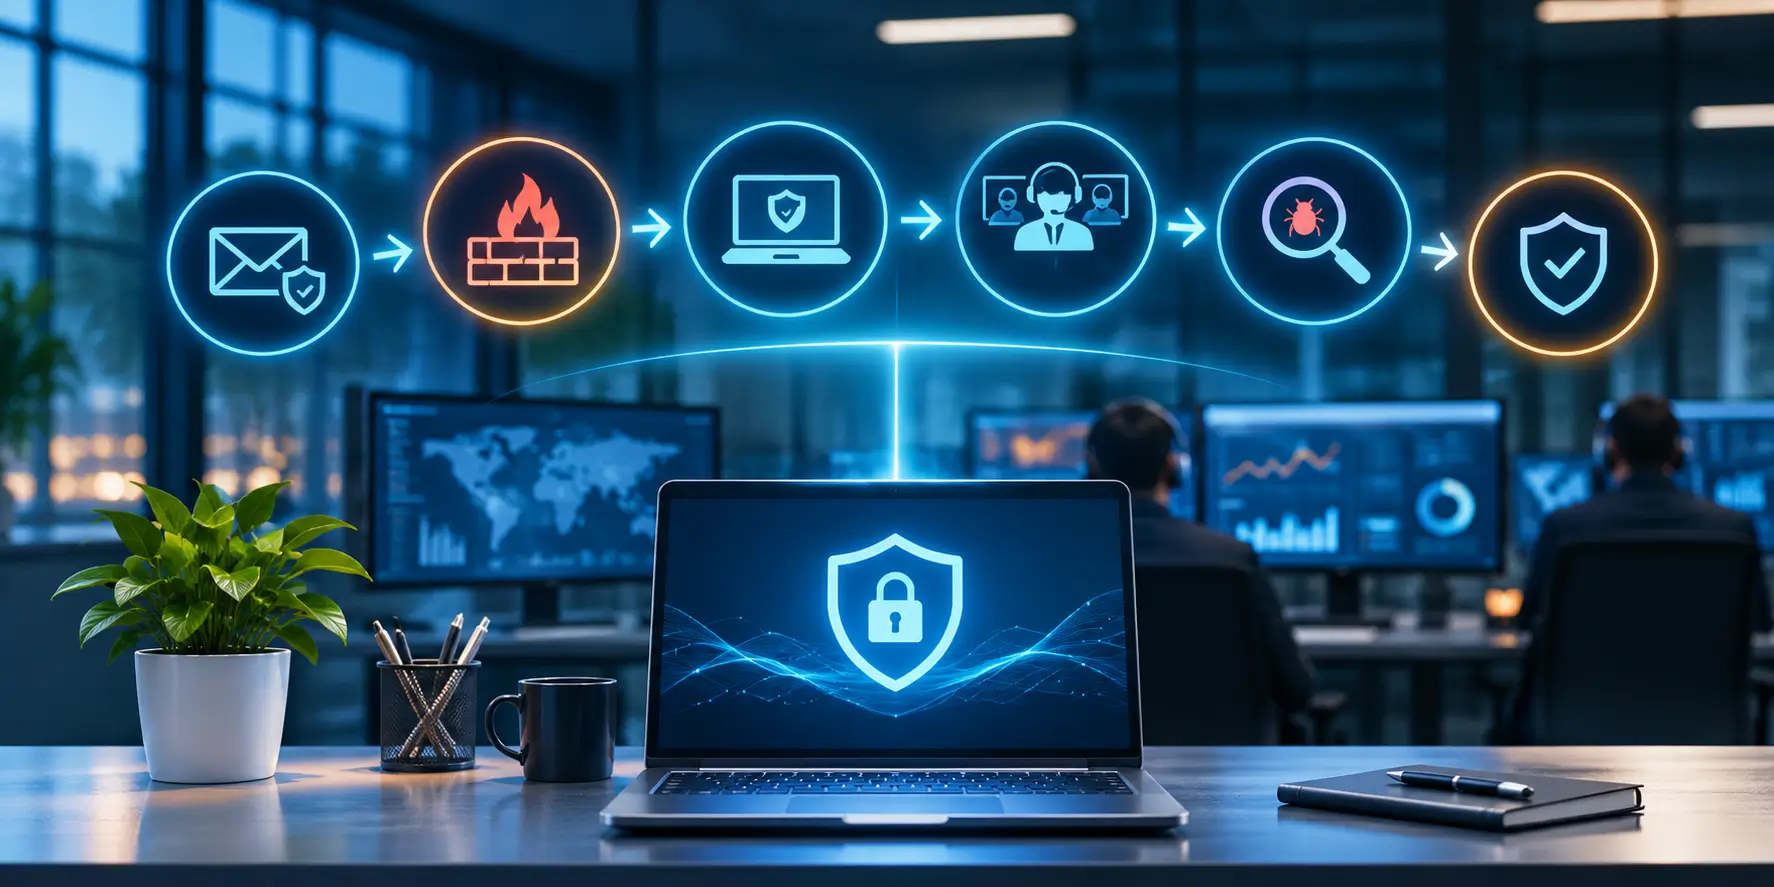
Your antivirus, firewall and email security each protect a different part of your business. EDR adds another layer by watching what’s happening on your computers and servers, helping identify suspicious activity that other tools may miss.
Businesses that need continuous security alert investigation can also explore our MDR services with 24/7 monitoring, which provide security professionals to investigate suspicious activity and coordinate appropriate responses.
Email Security → Firewall → EDR → SOC Monitoring → Threat Investigation → Response
Together, these security layers give your business better visibility into endpoint threats and help your team respond before incidents cause greater disruption.
To bring security events from endpoints, firewalls, servers and other connected systems together, businesses can also consider SIEM services for centralized security event monitoring and analysis.
When a business device gets infected, you need more than basic antivirus. BCS-IP helps local businesses strengthen endpoint protection and investigate suspicious activity.
Get local IT and cybersecurity expertise to protect your business computers and servers.
Businesses that also need ongoing infrastructure management and technical support can explore our managed IT services for Austin businesses.
Basic antivirus may not catch every threat. BCS-IP’s managed EDR services help protect your business computers and servers by detecting suspicious activity, investigating threats and containing compromised devices before they disrupt your operations.
Not sure whether your current endpoint protection covers every business device? Start with a cybersecurity risk assessment to identify potential security gaps.