Your security tools can flag suspicious activity. But who’s watching those alerts when your team is busy—or the office is closed? MDR will give you security professionals who continuously monitor alerts, investigate unusual activity, and help coordinate the right response.
Explore our broader cybersecurity services in Austin to understand how MDR can fit into a layered security strategy.
MDR stands for Managed Detection and Response. It puts security professionals behind your security tools to monitor alerts and investigate suspicious activity.
MDR Services Austin TX gives your business ongoing security monitoring without needing to build an in-house 24/7 SOC.
For broader technology management, see our managed IT services for Austin businesses.
01
EDR, SIEM, Microsoft 365, or another security tool detects activity that may need attention.
02
03
04
A normal-looking login can hide account takeover. Analysts compare location, device, timing, MFA activity related access patterns. This detects suspicious use.
A dangerous email can reach an employee despite filtering. MDR analysts investigate clicks, account activity, endpoint behavior, as well as follow-up signs
Attackers may move quietly between systems after gaining access. Analysts examine authentication patterns, account usage, and connected activity.
One unusual process may mean nothing—or signal compromise. Analysts trace process activity, scripts, parent processes, and relate
Administrative access deserves closer scrutiny. Our expert analysts investigate unexpected privilege changes, unusual administrative actions.
Threat activity doesn’t follow office hours. Continuous SOC monitoring will ensure unusual activity appearing overnight or during weekends receives attention.
A suspicious login at midnight or an endpoint alert after hours must not wait until the next morning. MDR services will give your business the perfect security professionals who can review alerts and escalate real threats.
MDR analysts filter routine notifications from genuinely suspicious activity. With this, your IT team can simply focus on incidents that deserve attention.
24/7 SOC analysts review suspicious activity outside business hours instead of leaving alerts for your team to discover the next morning.
MDR investigates the process, user activity, and related events to determine if an endpoint alert points to a real compromise.
Analysts examine unusual locations, devices, timing, and MFA activity, as well as related access to id
MDR connects related activity across accounts, endpoints, and network events to uncover patterns hidden insid
After a suspicious click, analysts check related account along with endpoint activity to determine if the threat moved beyond the email.
MDR adds dedicated security analysts who can investigate complex alerts without requiring your business to build an internal SOC.
Analysts assess severity, evidence, and potential impact so meaningful incidents receive the appropriate level of attention.
Continuous monitoring will give you security events a path to investigation during evenings or weekends when your staff may be unavailable.
MDR actually goes beyond notification by simply investigating what happened and escalating when further response is warranted
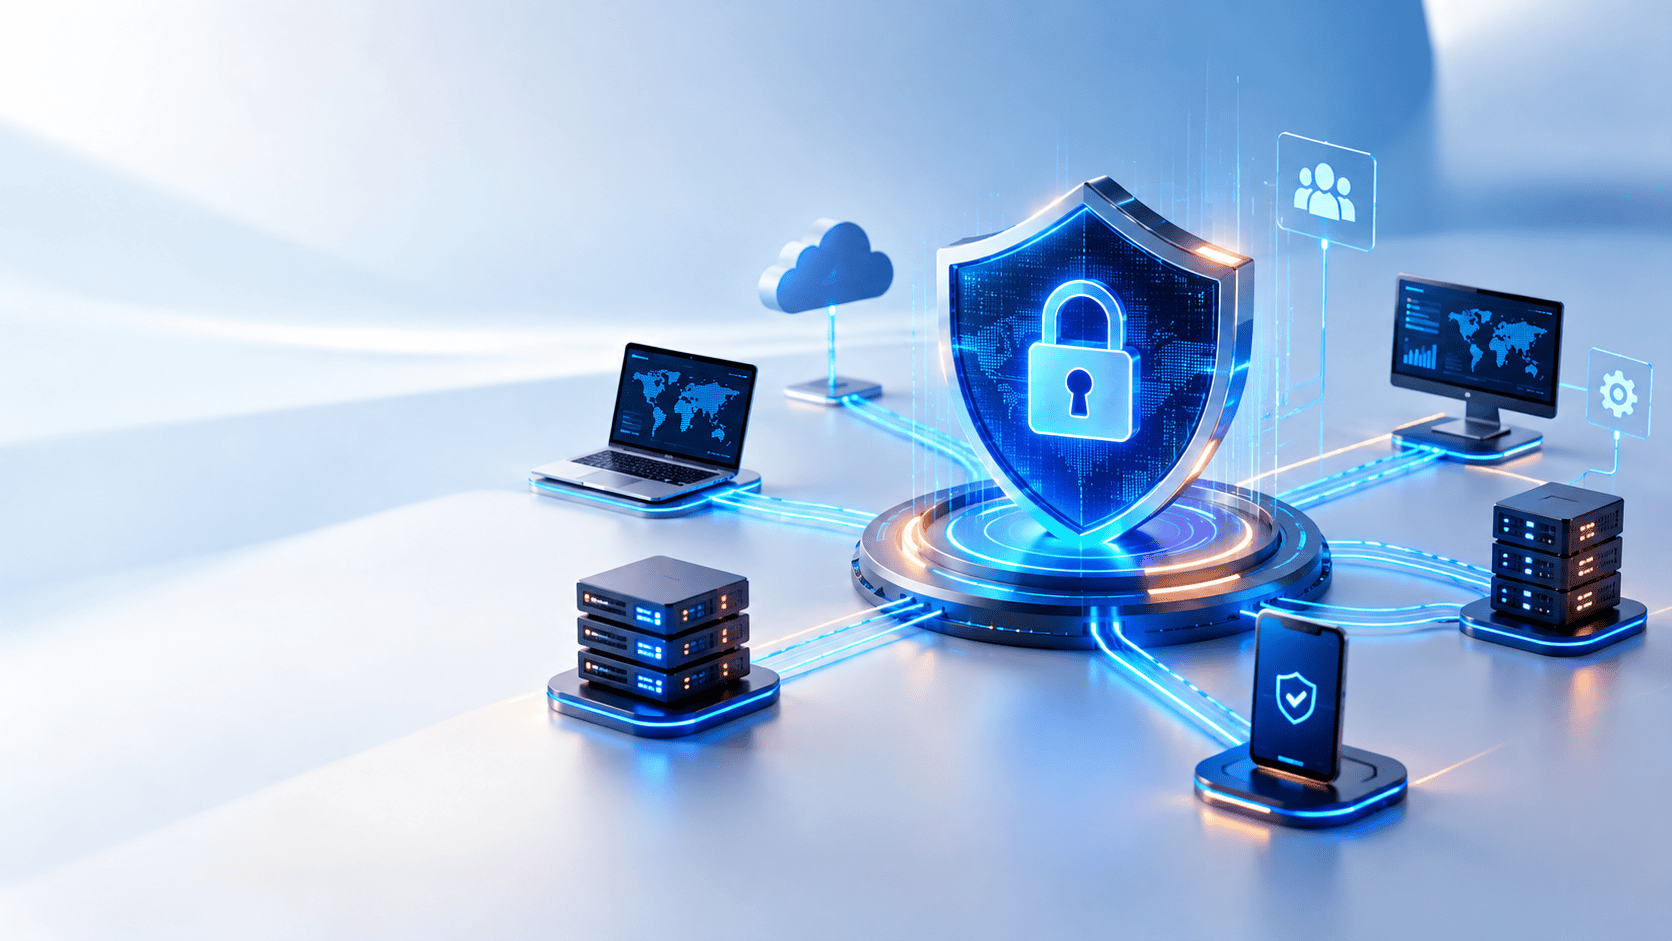
No single security layer catches everything. MDR will work alongside your existing controls and give your business the continuous monitoring and investigation.
Email Security → MFA → EDR → Firewall → SIEM → MDR/SOC → Backup
Together, these layers help prevent, detect, investigate, contain, and recover from security incidents.
A serious alert can quickly turn into a compromised laptop or an affected server. When security and IT issues overlap, you can actually need a team that can handle both tasks.
MDR monitoring backed by local IT expertise—so security issues don’t stop at the alert.
MDR provides continuous threat monitoring, investigation, and response support from security professionals.
It means your team can monitor security alerts 24/7, including nights and weekends.
government contractors and recommended for all Houston businesses to ensure long-term support and cybersecurity.